Cybersecurity built for critical infrastructure. Ready for yours.
The protection of a full security team, without having to build one. TITAN and our 24/7 SOC watch over your OT and IT so your team can focus on what they do best.
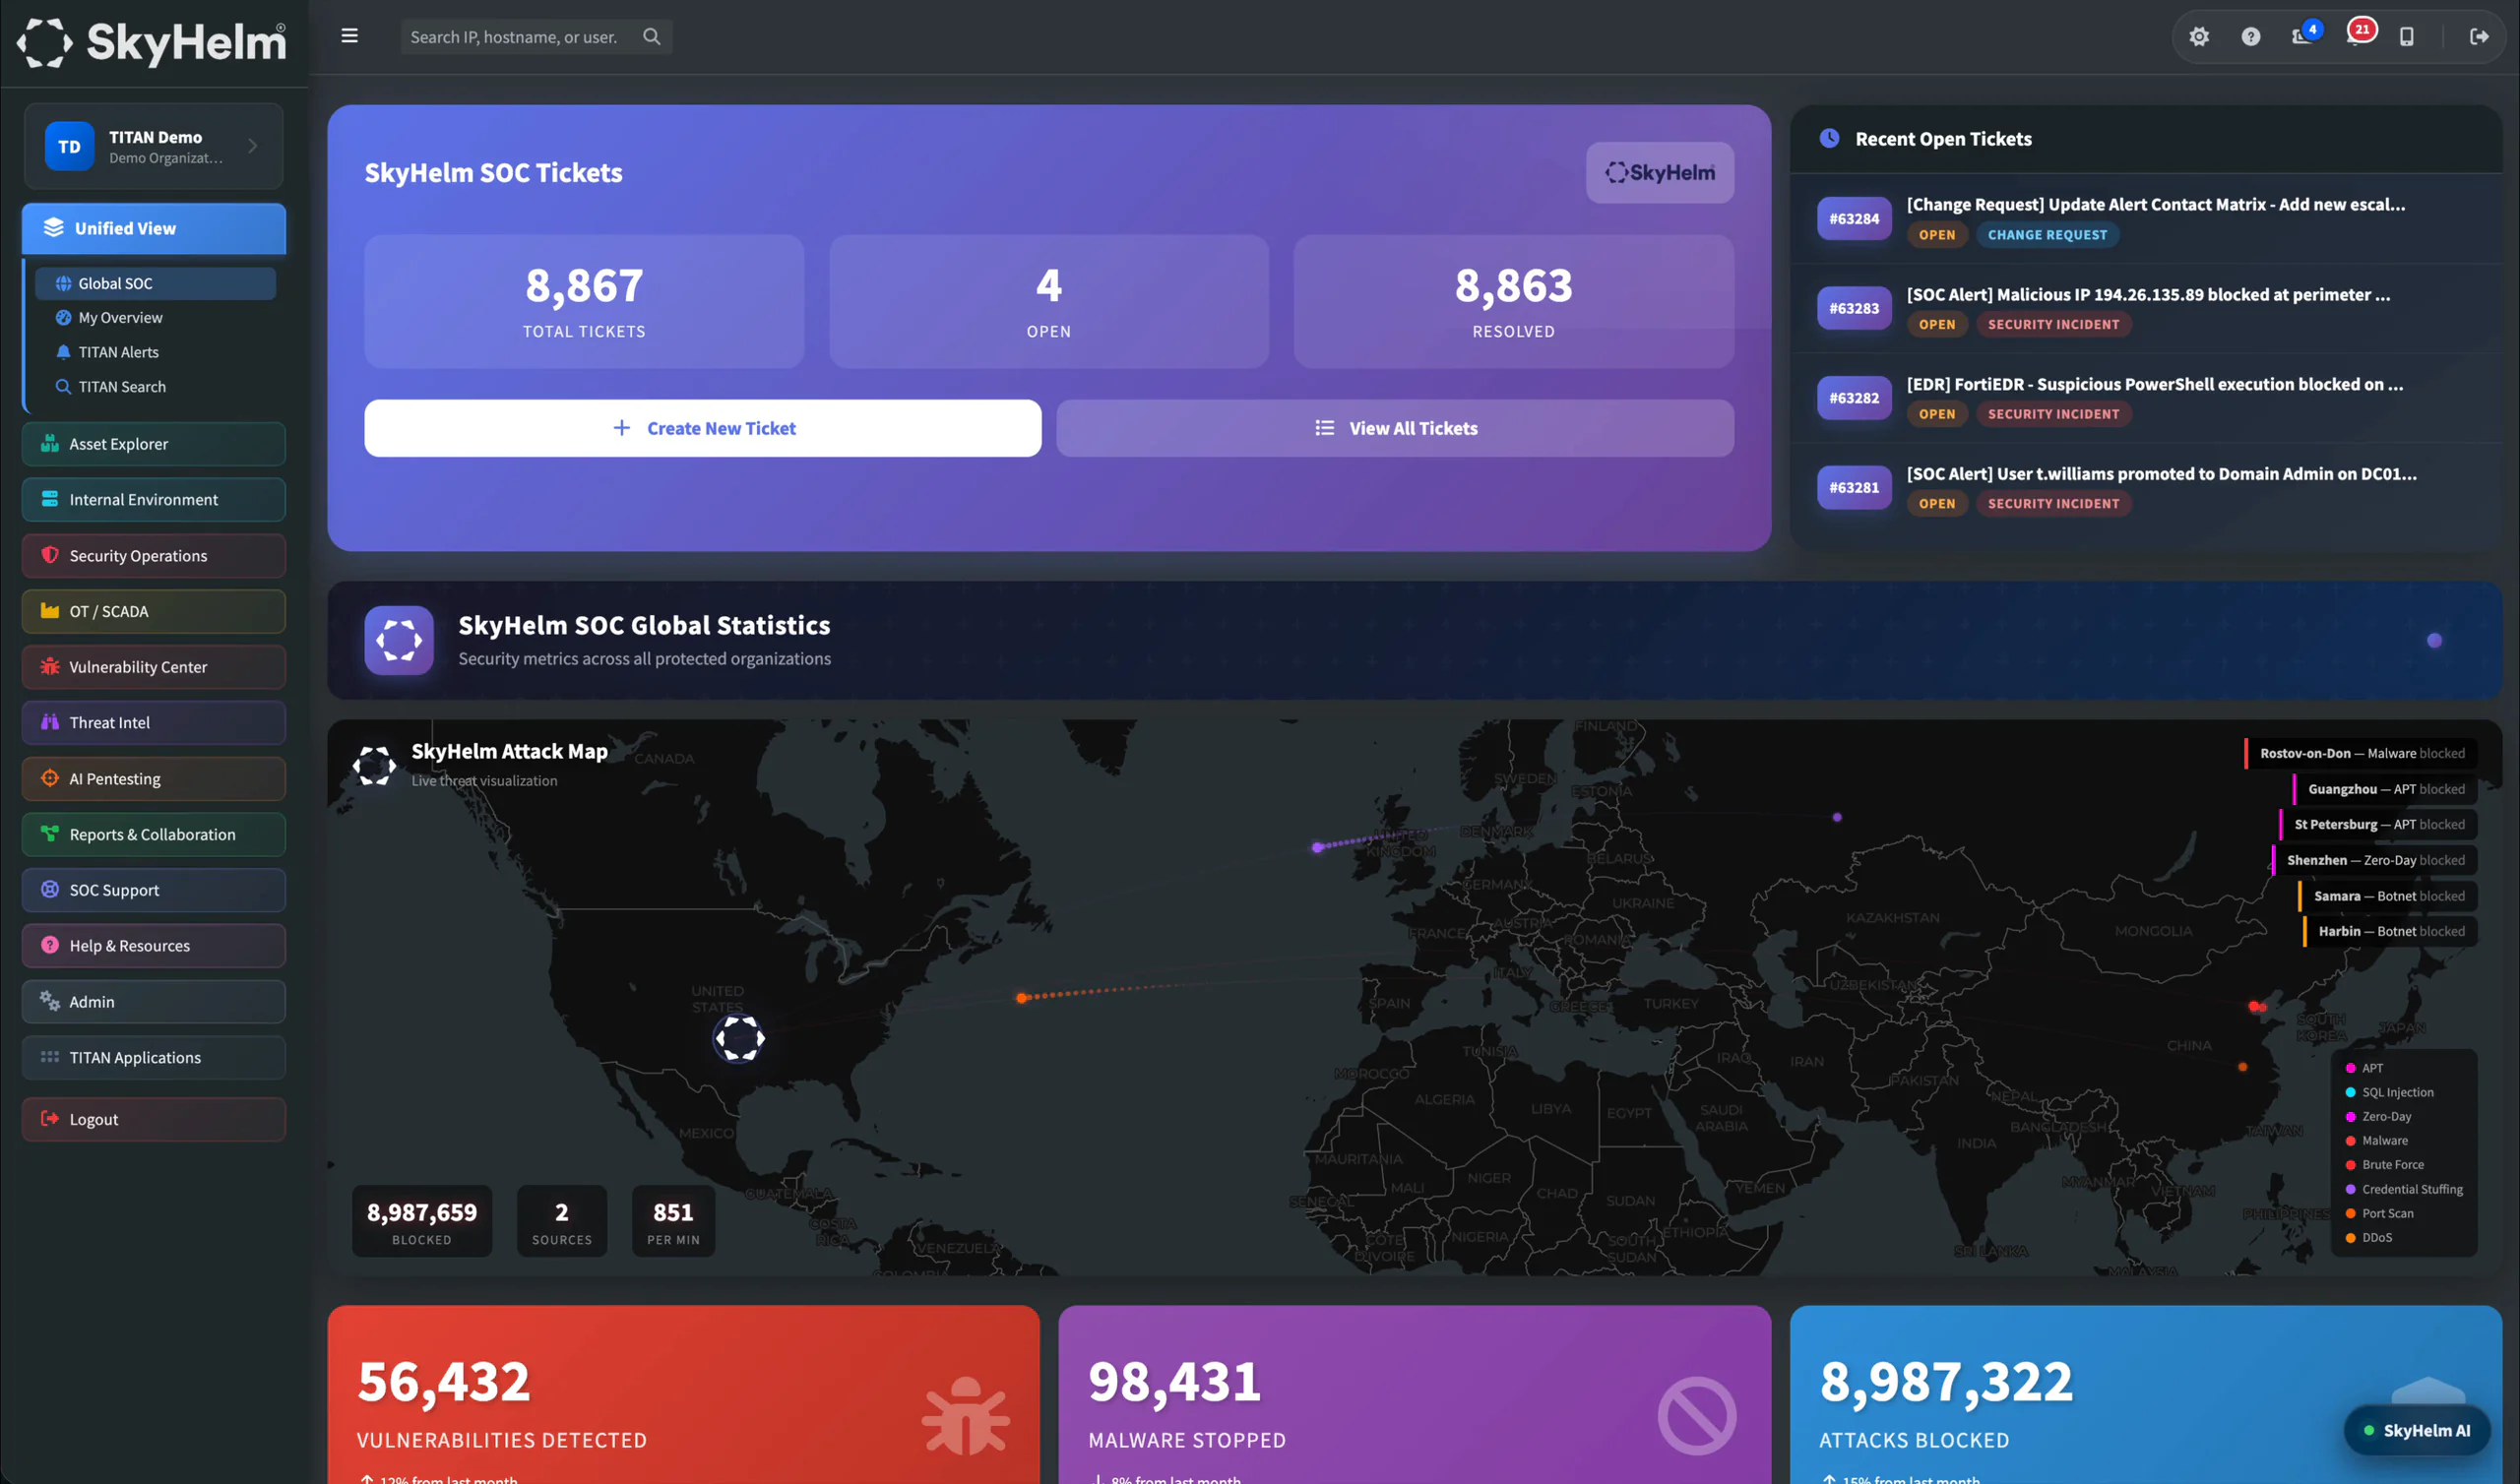
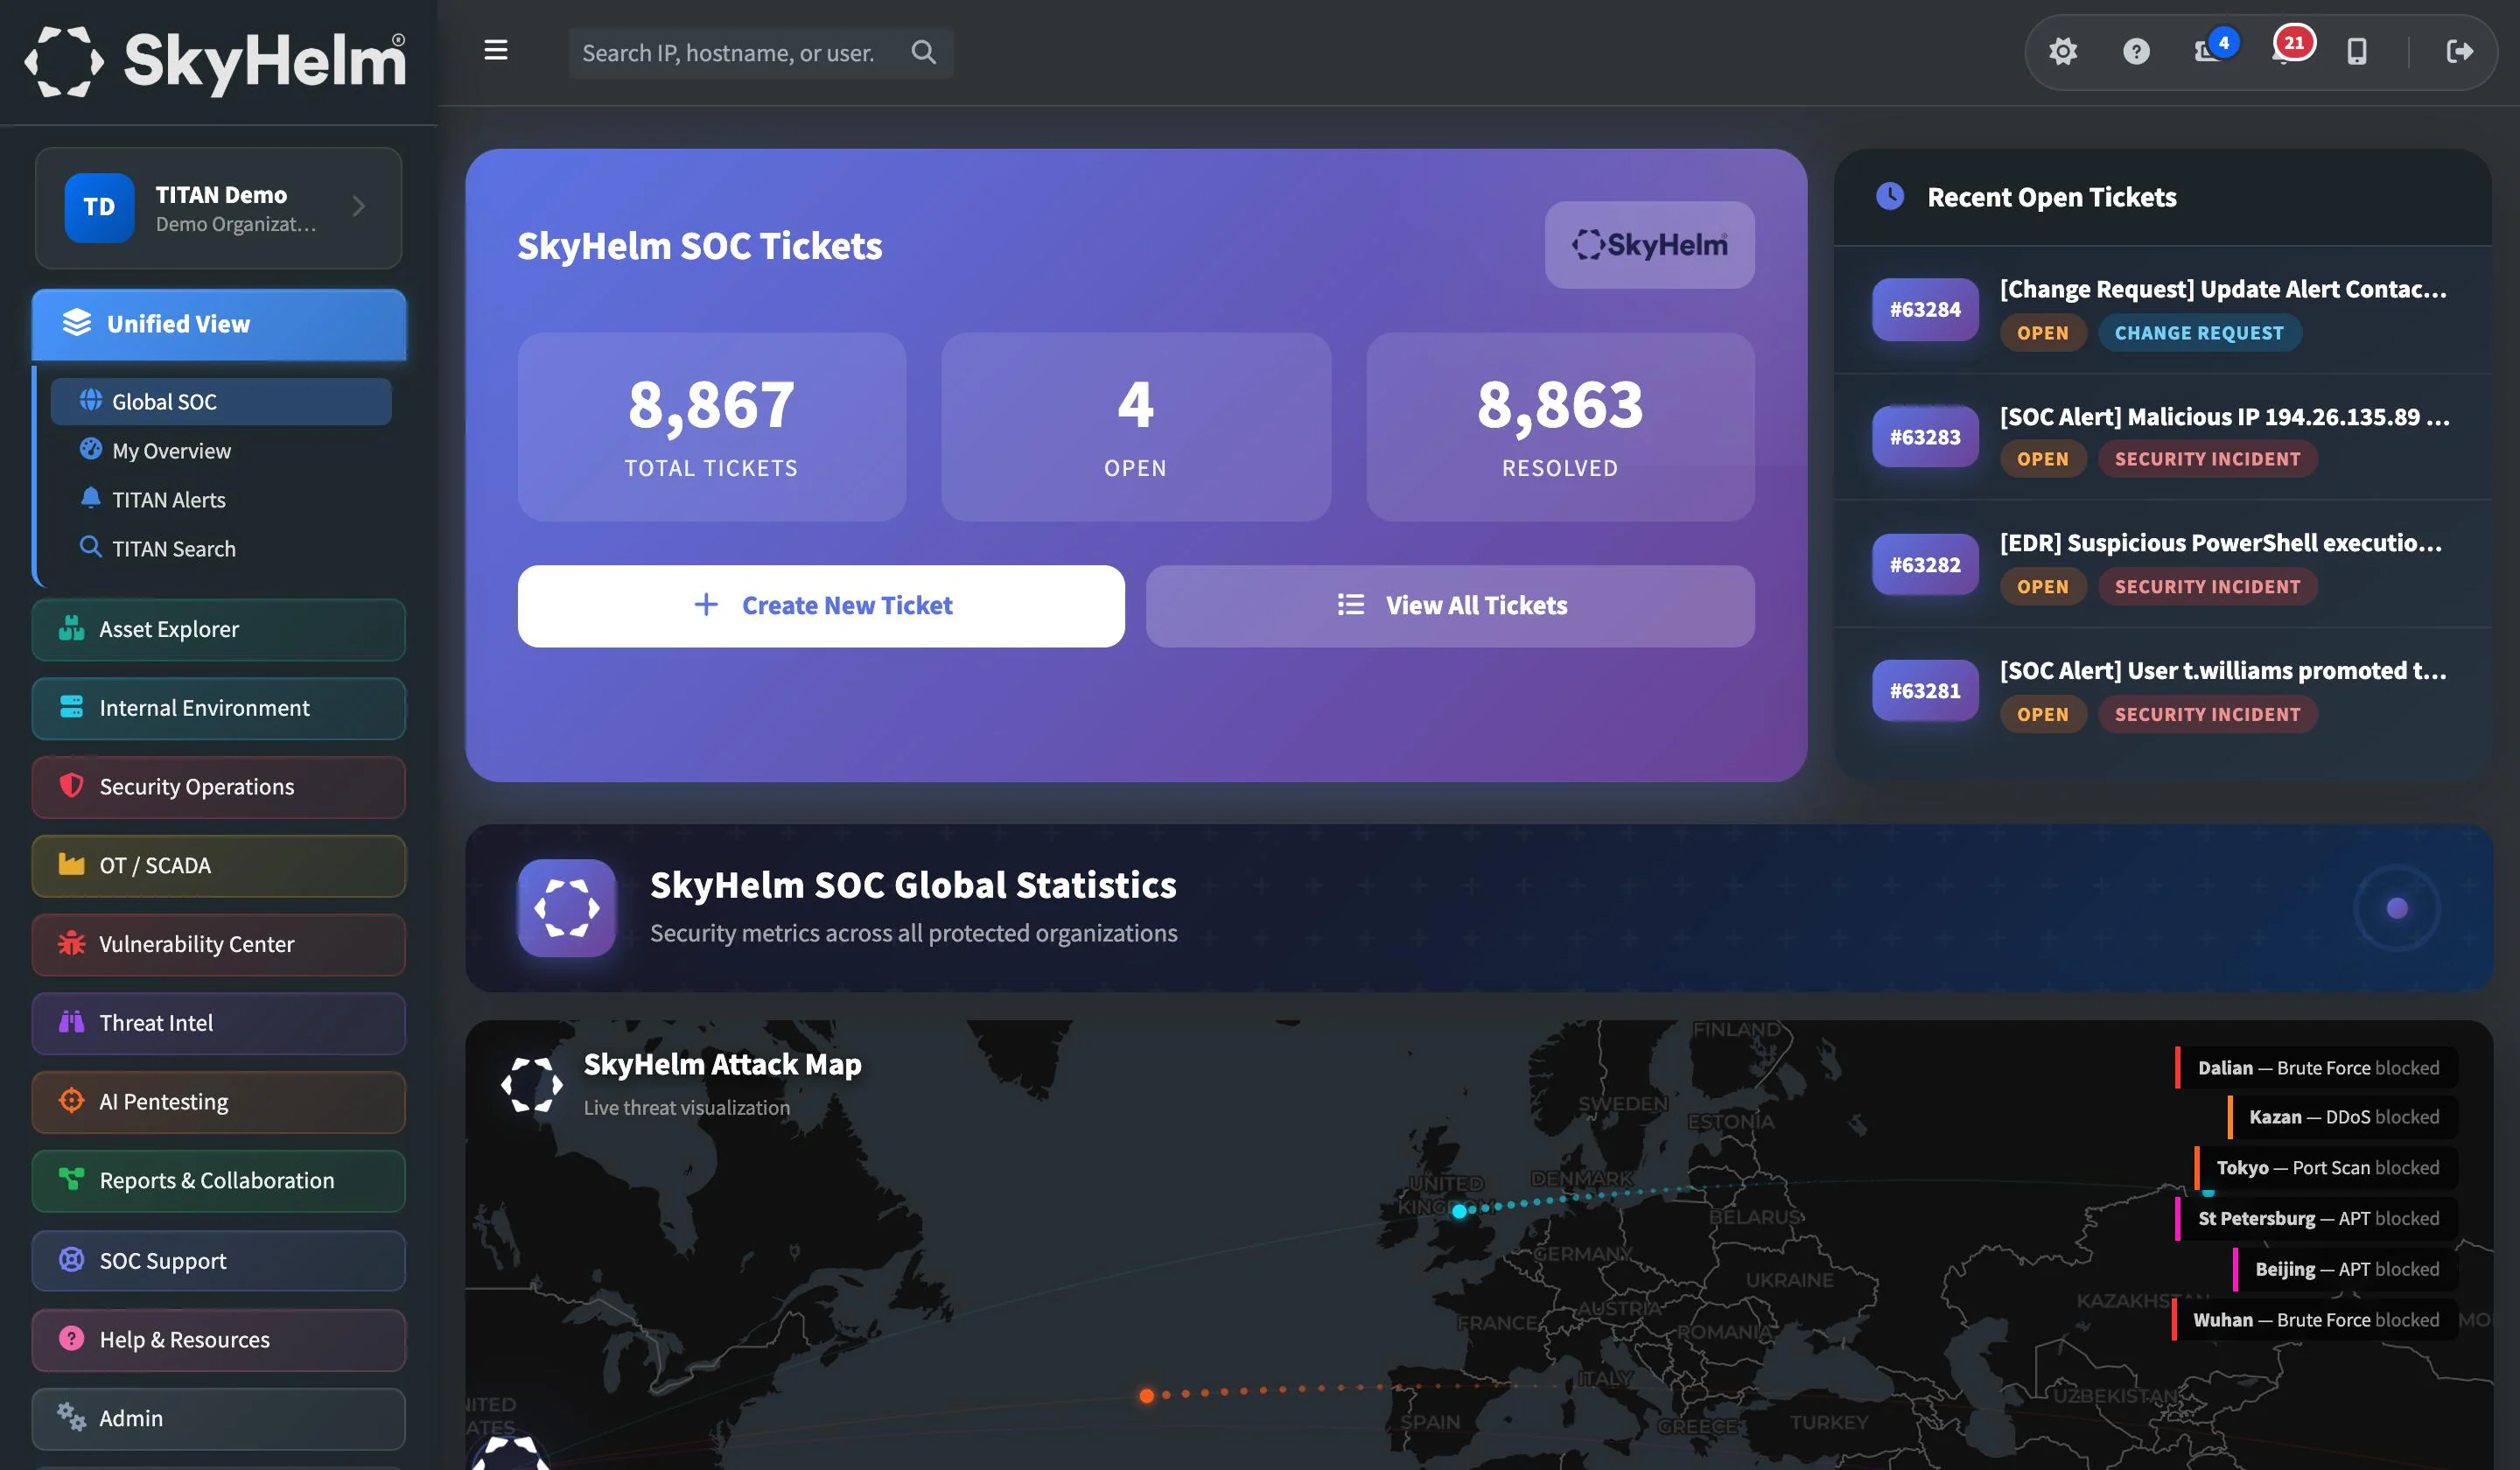
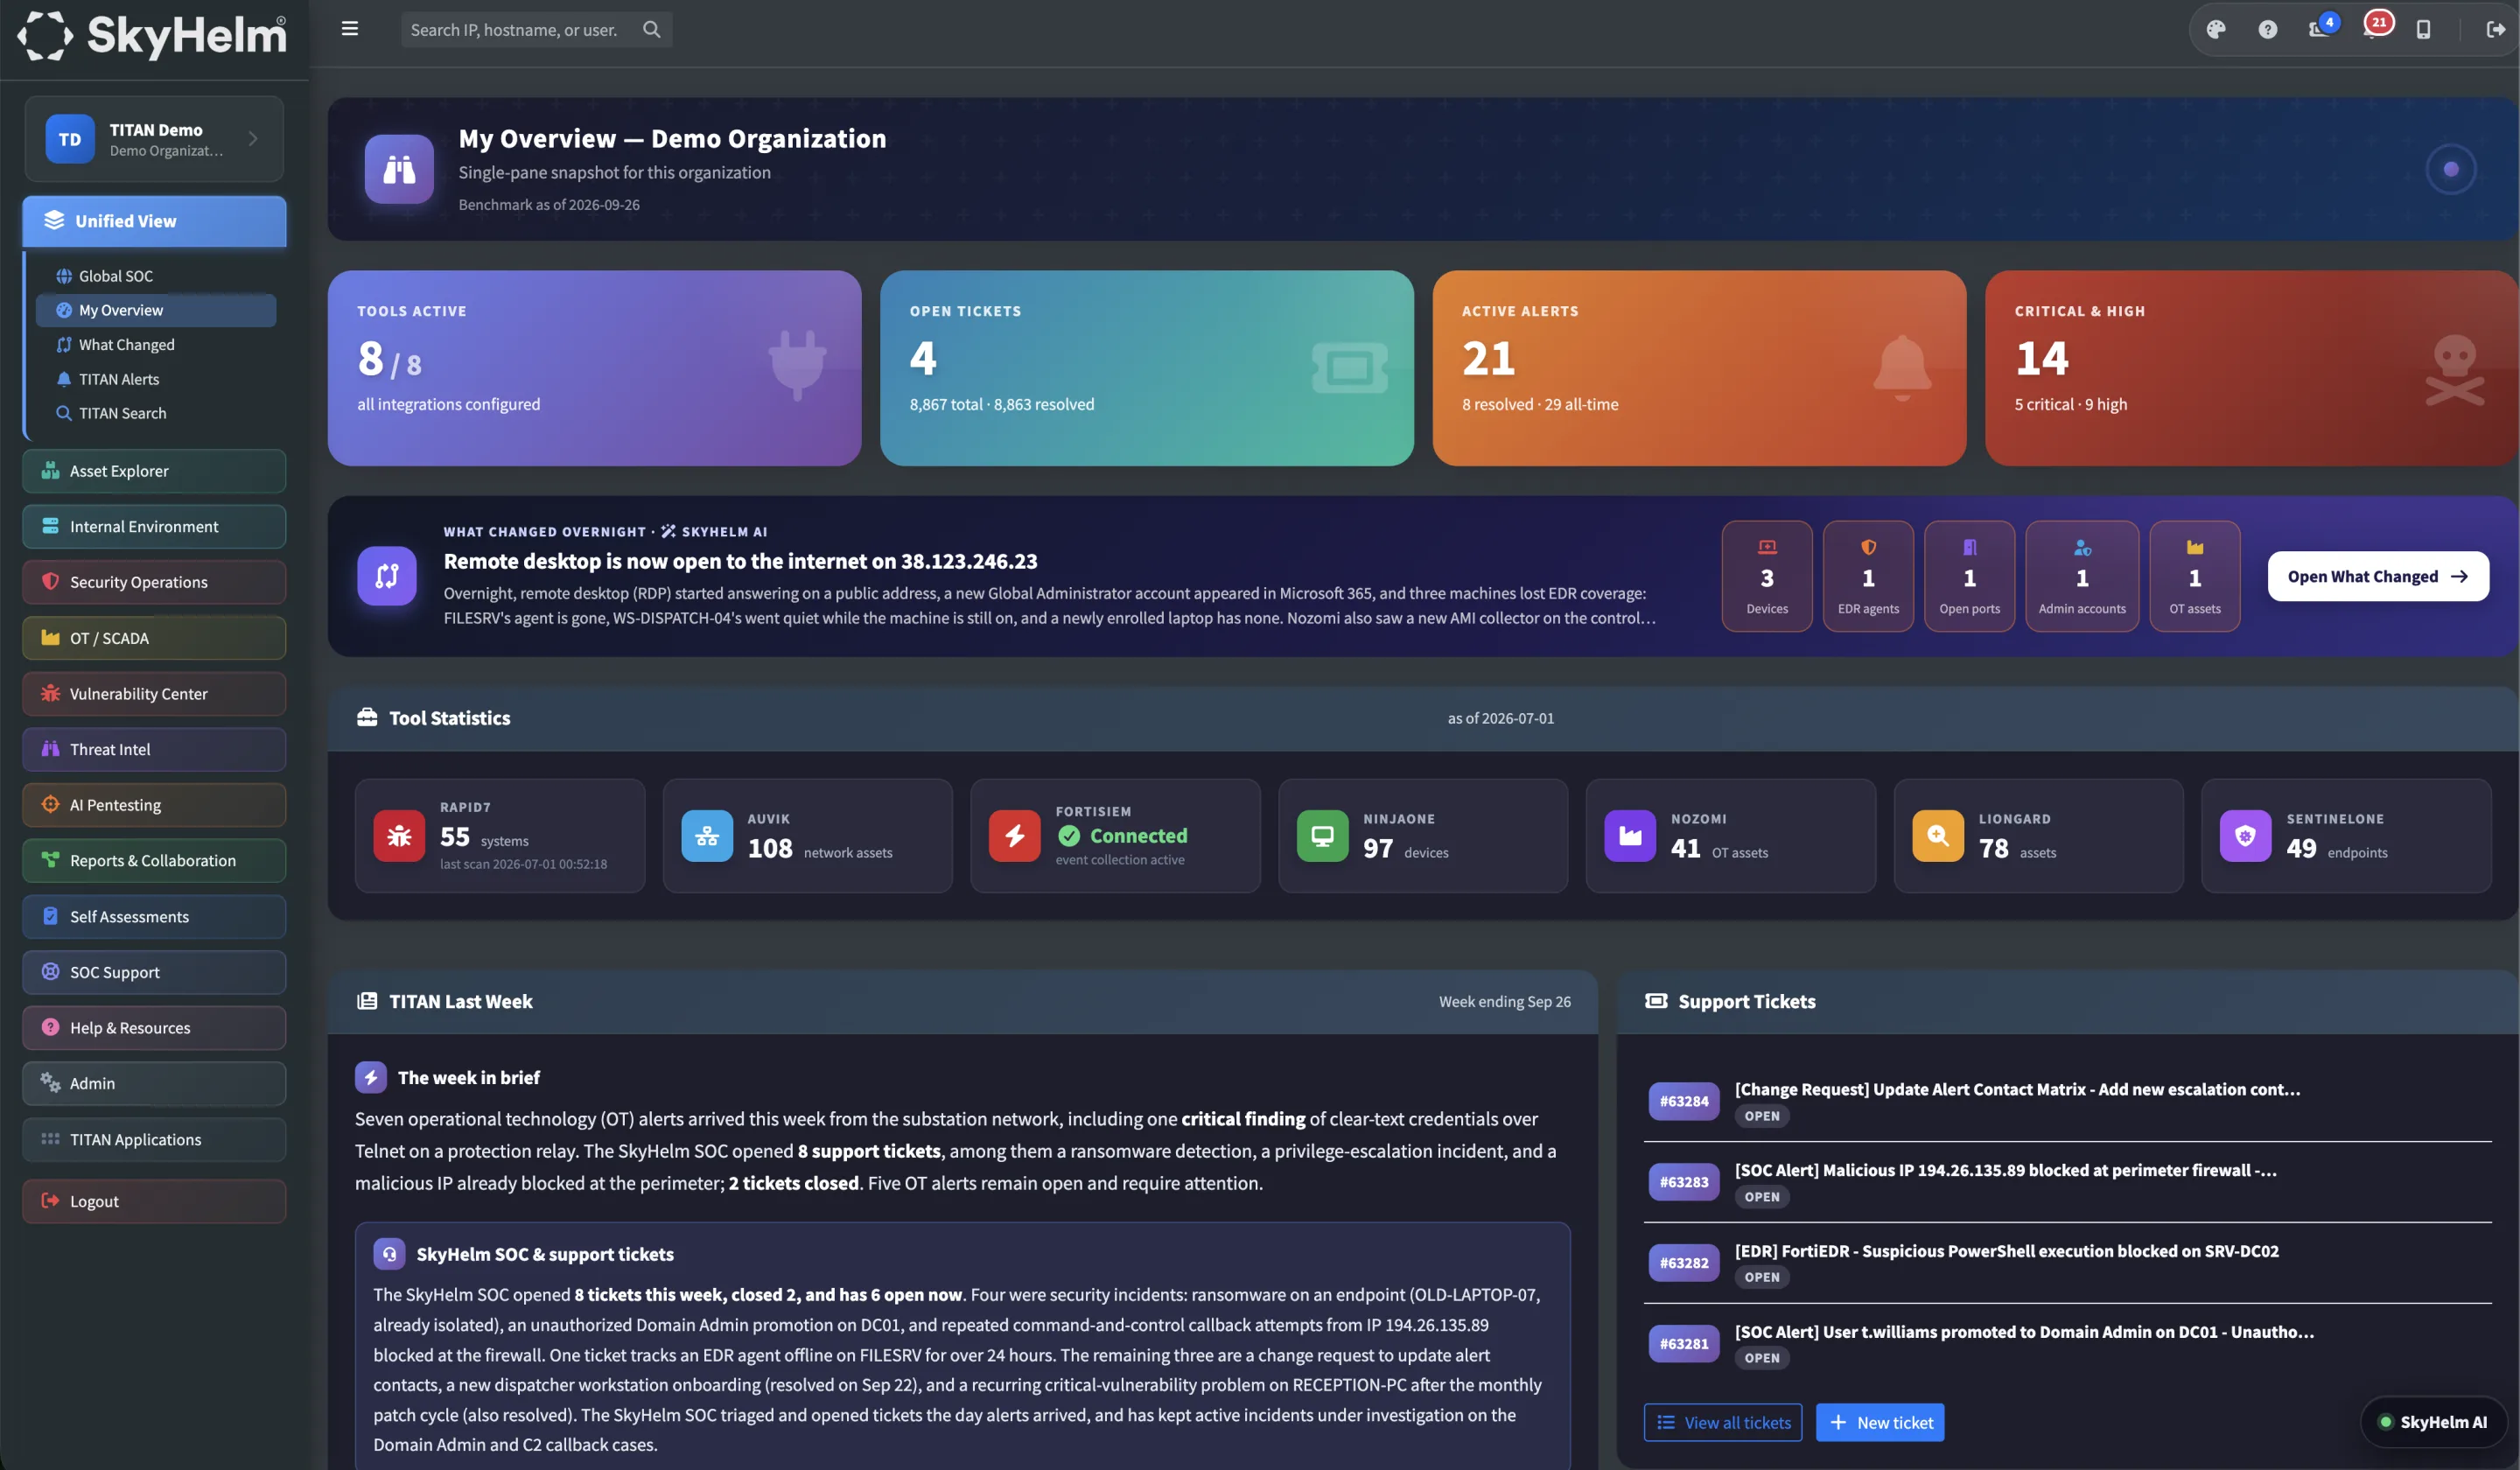
TITAN brings every security tool you run into one pane of glass. Our analysts watch it around the clock. You get back to serving your members, customers, and community.
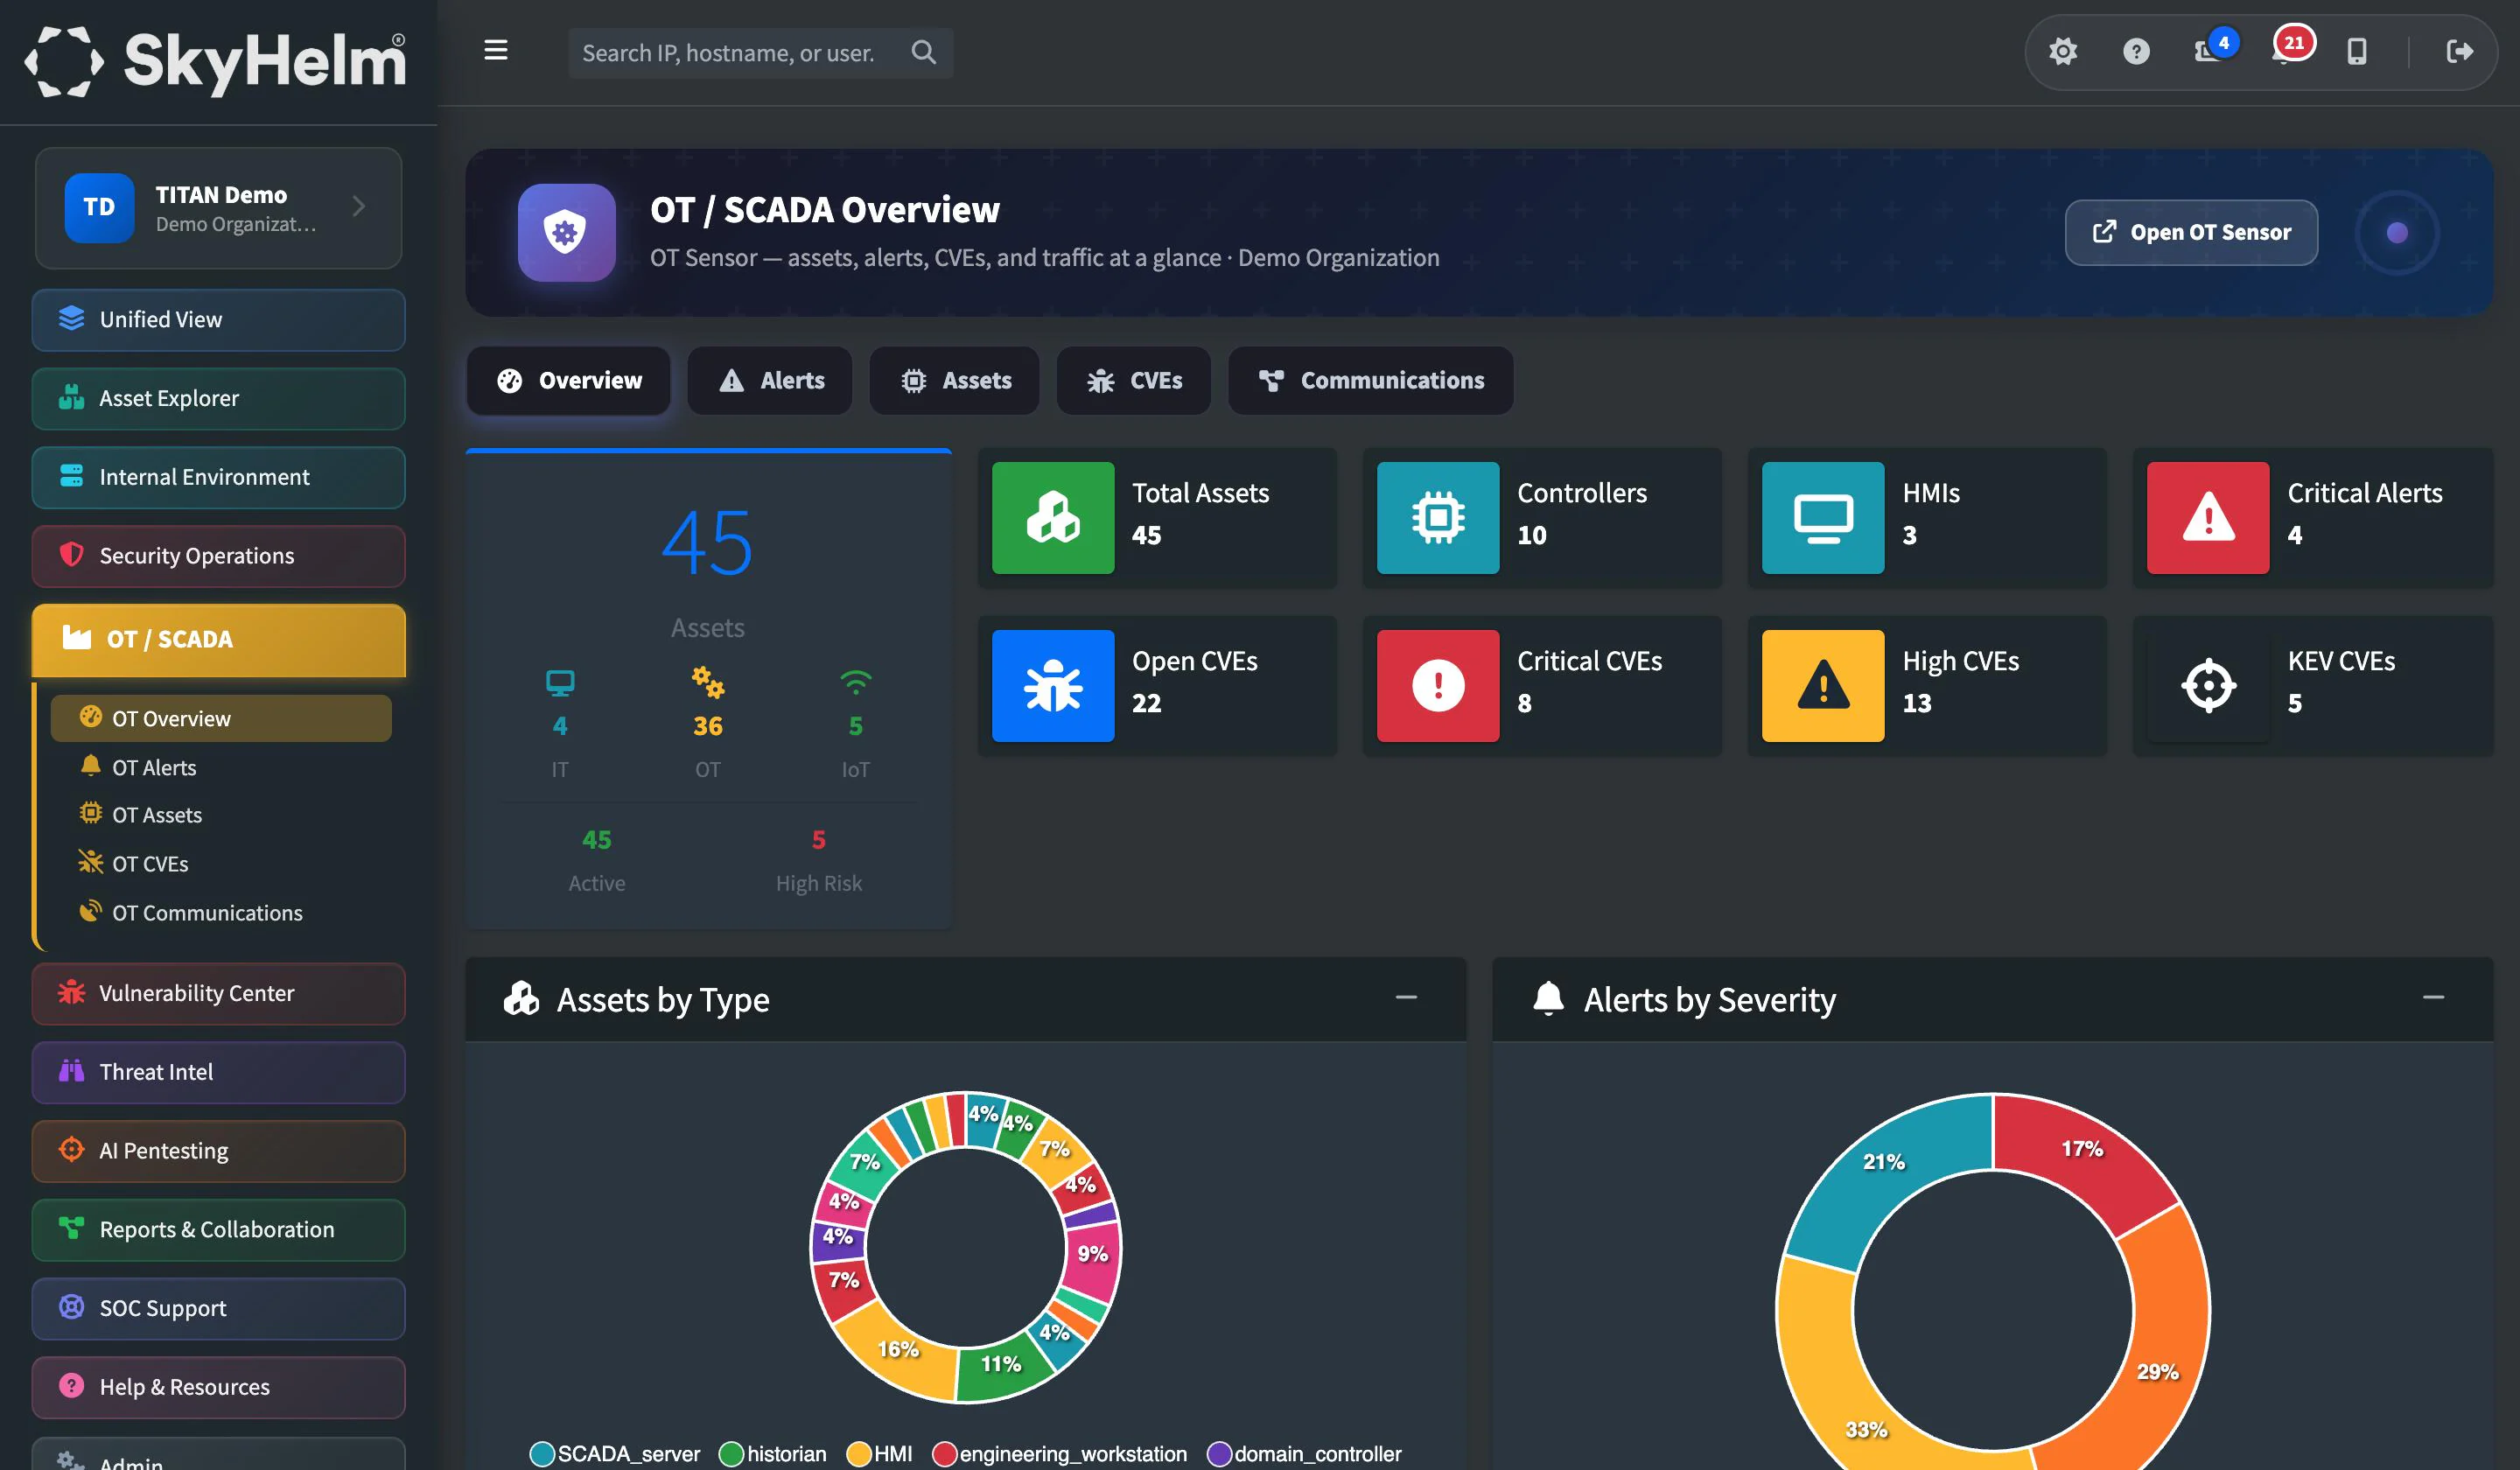
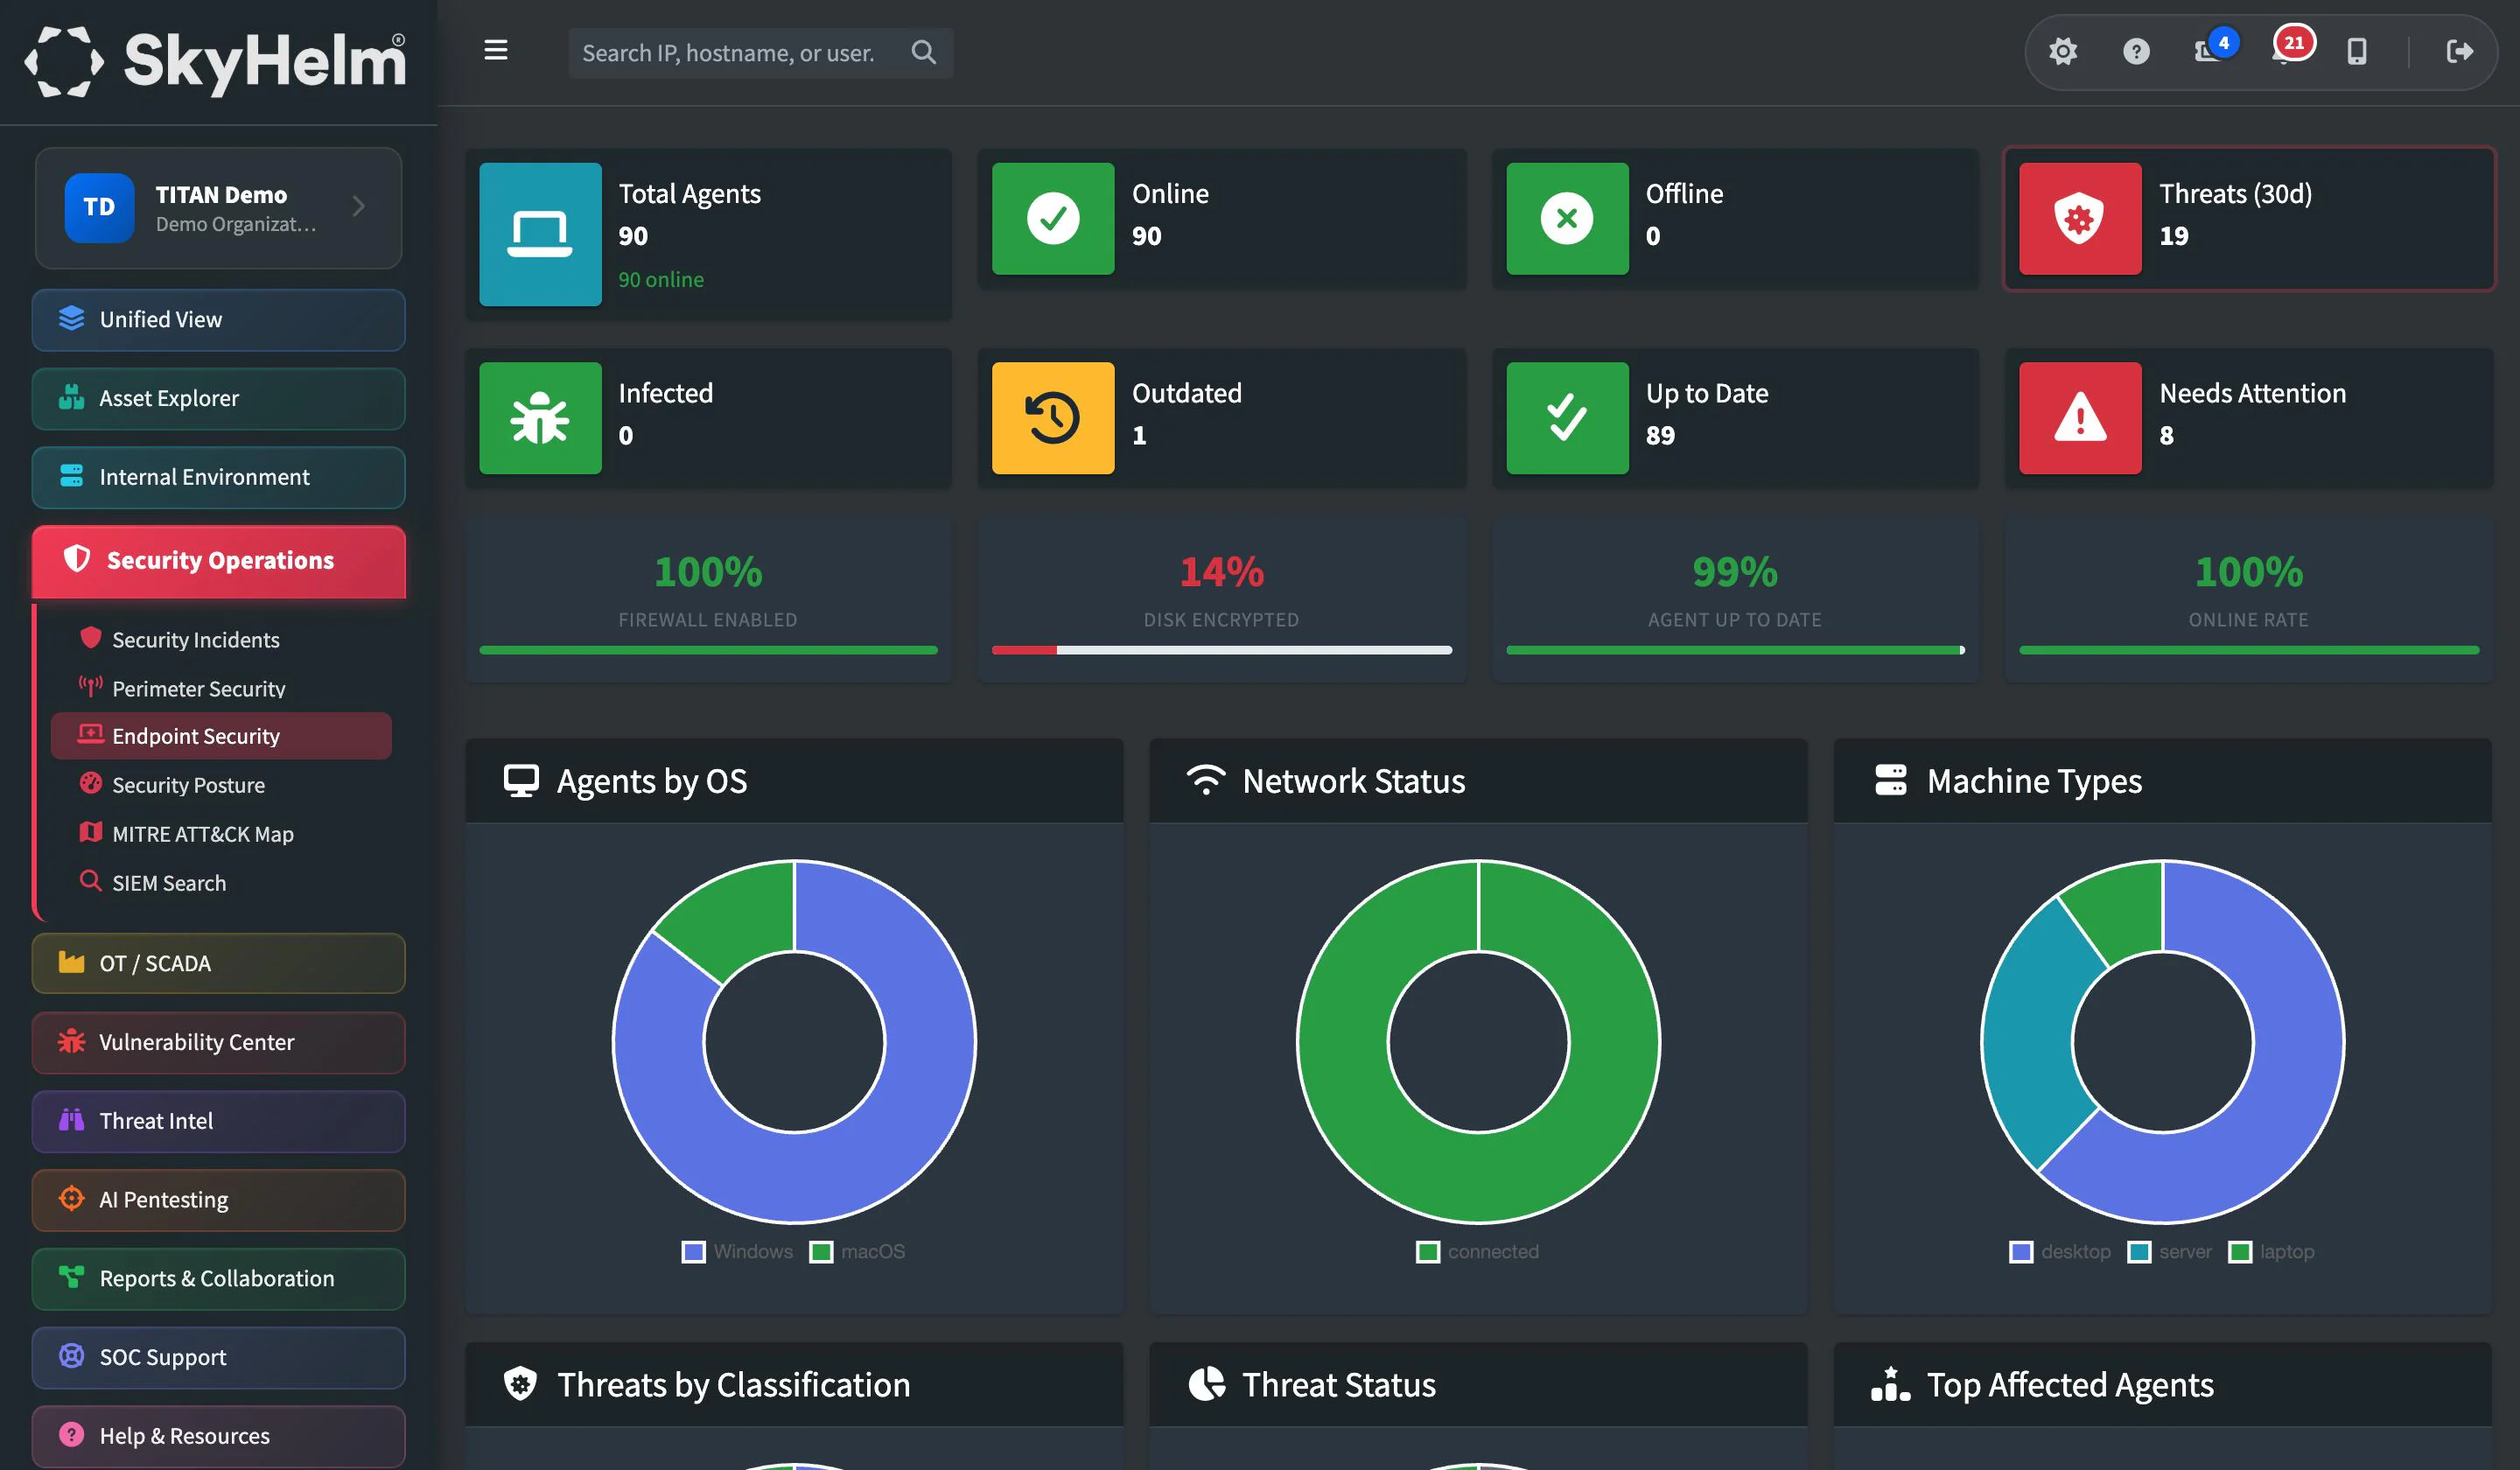
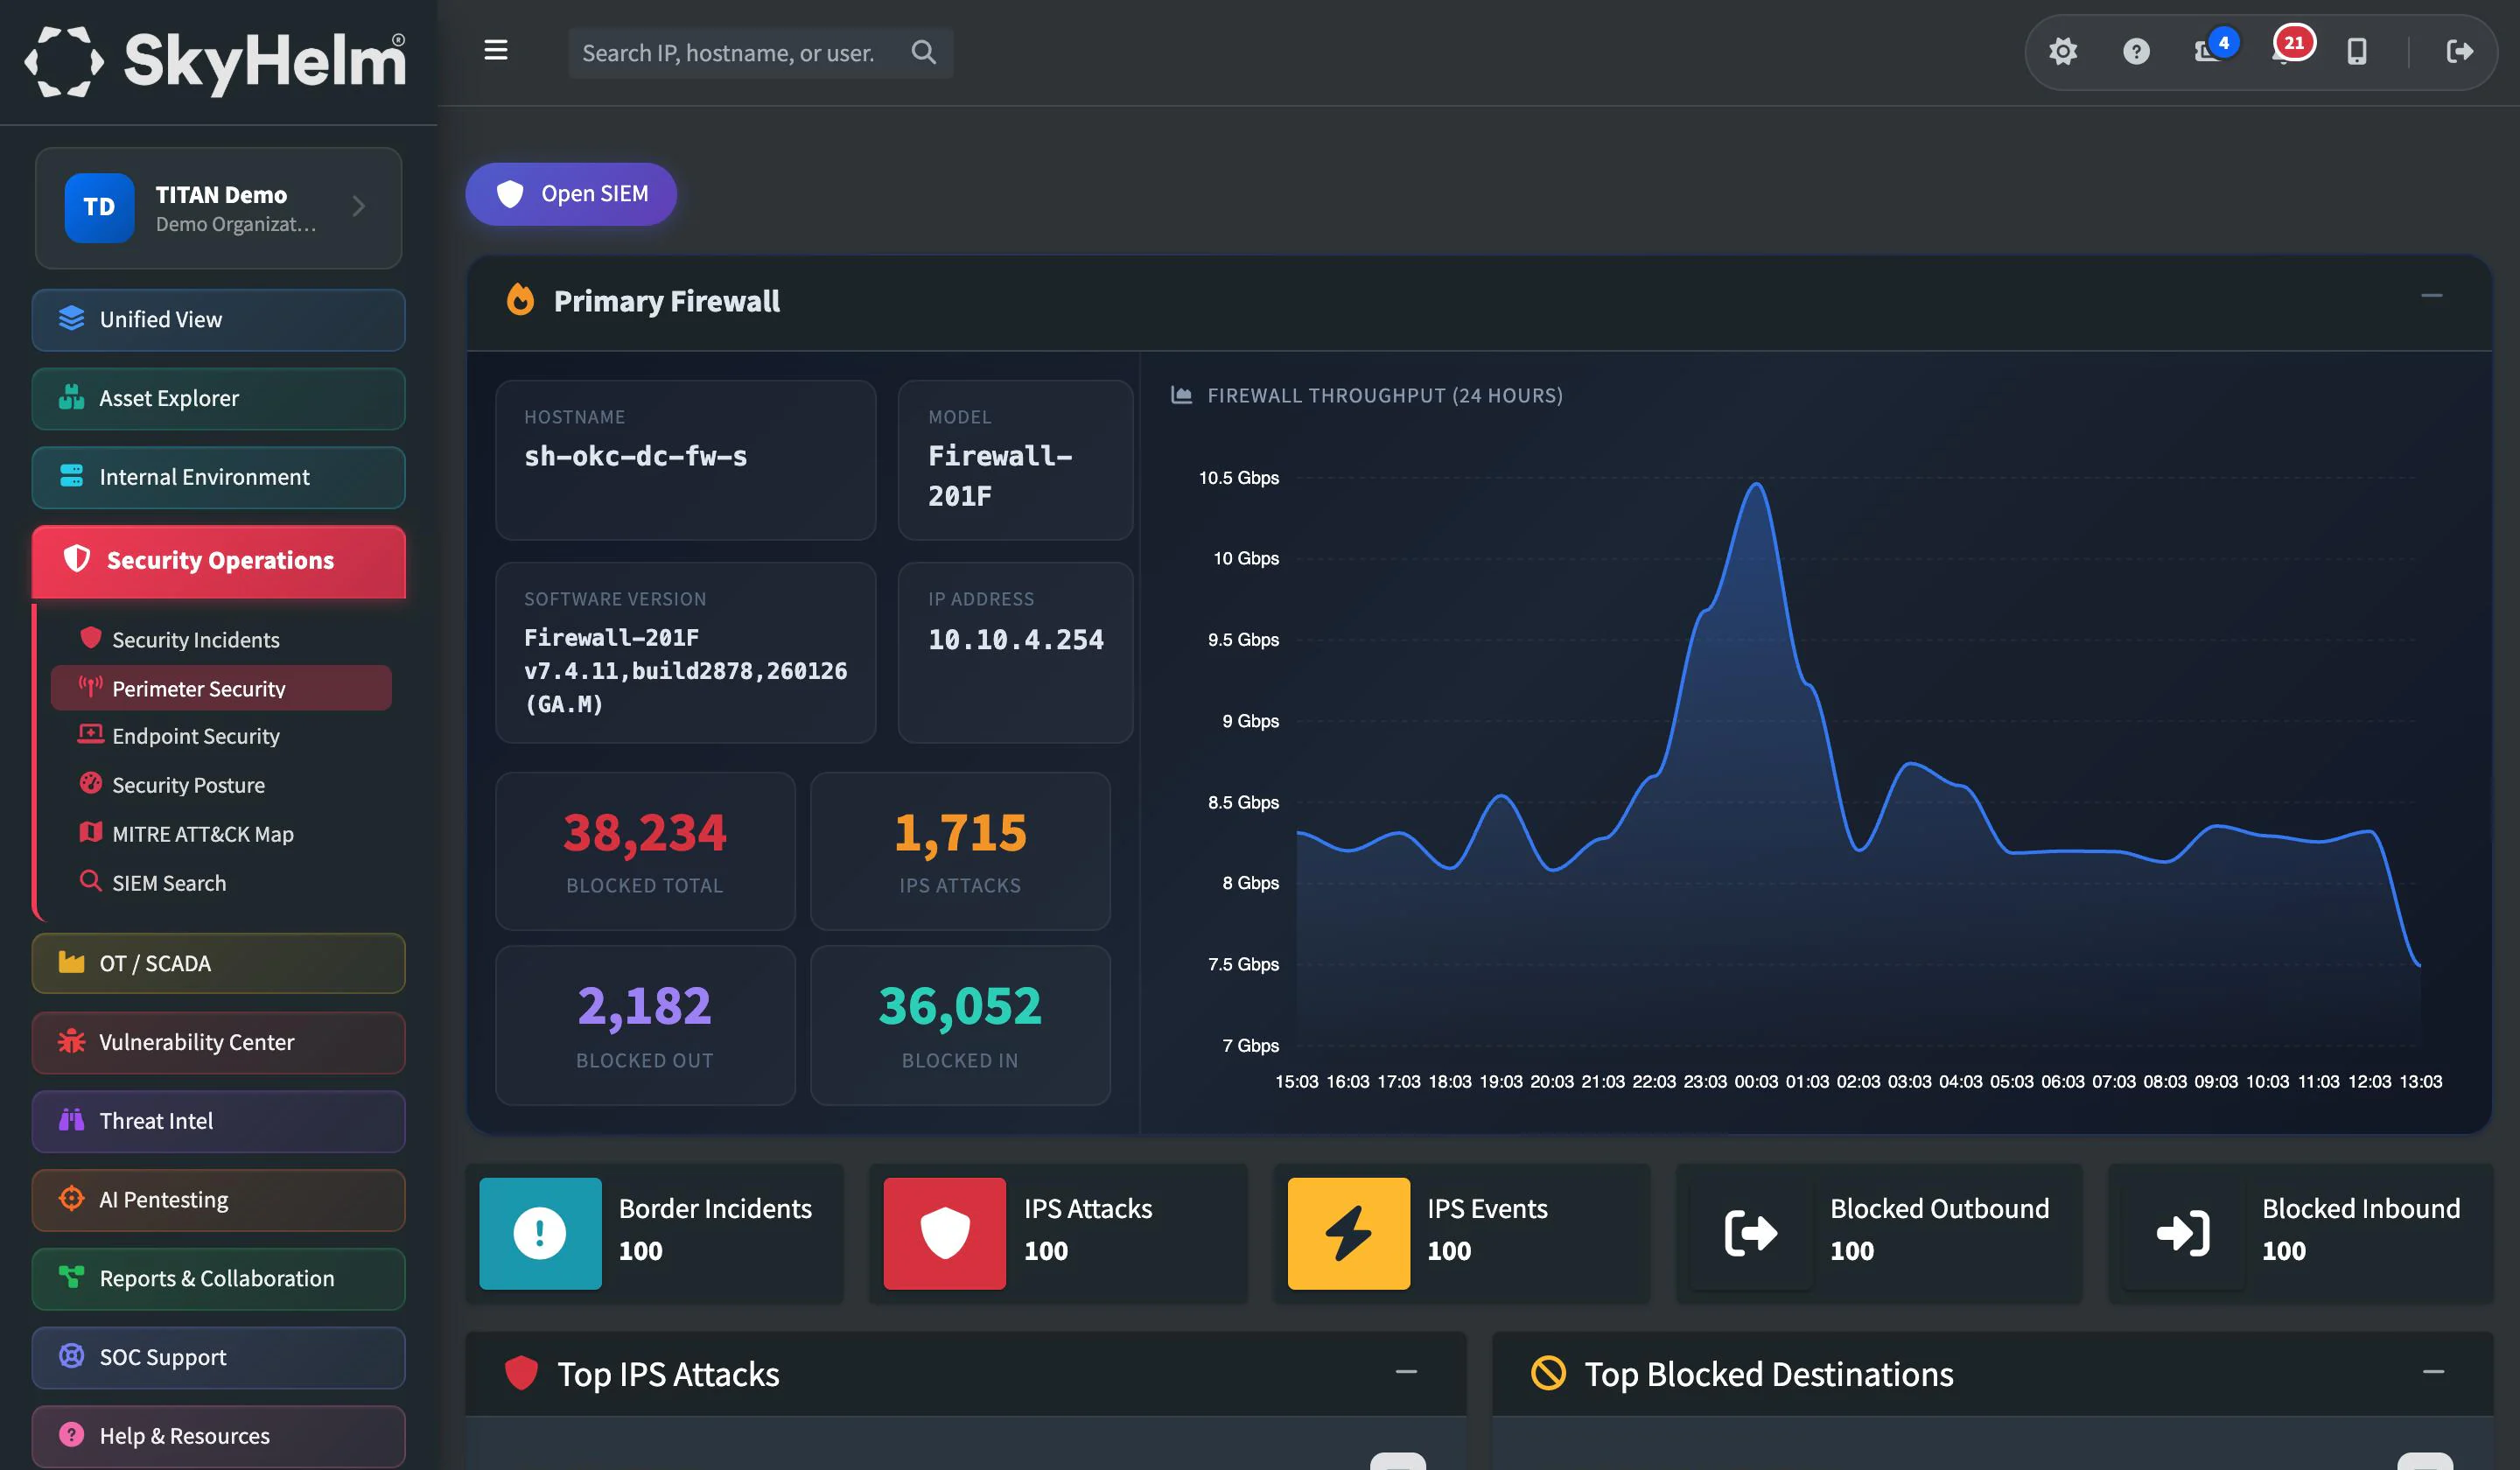
Firewalls. Endpoints. Substations. Logs.
You run dozens of tools, each with its own screen and its own alerts.
Pulled into one platform.
TITAN connects them, correlates them and ranks what matters first.
Watched around the clock.
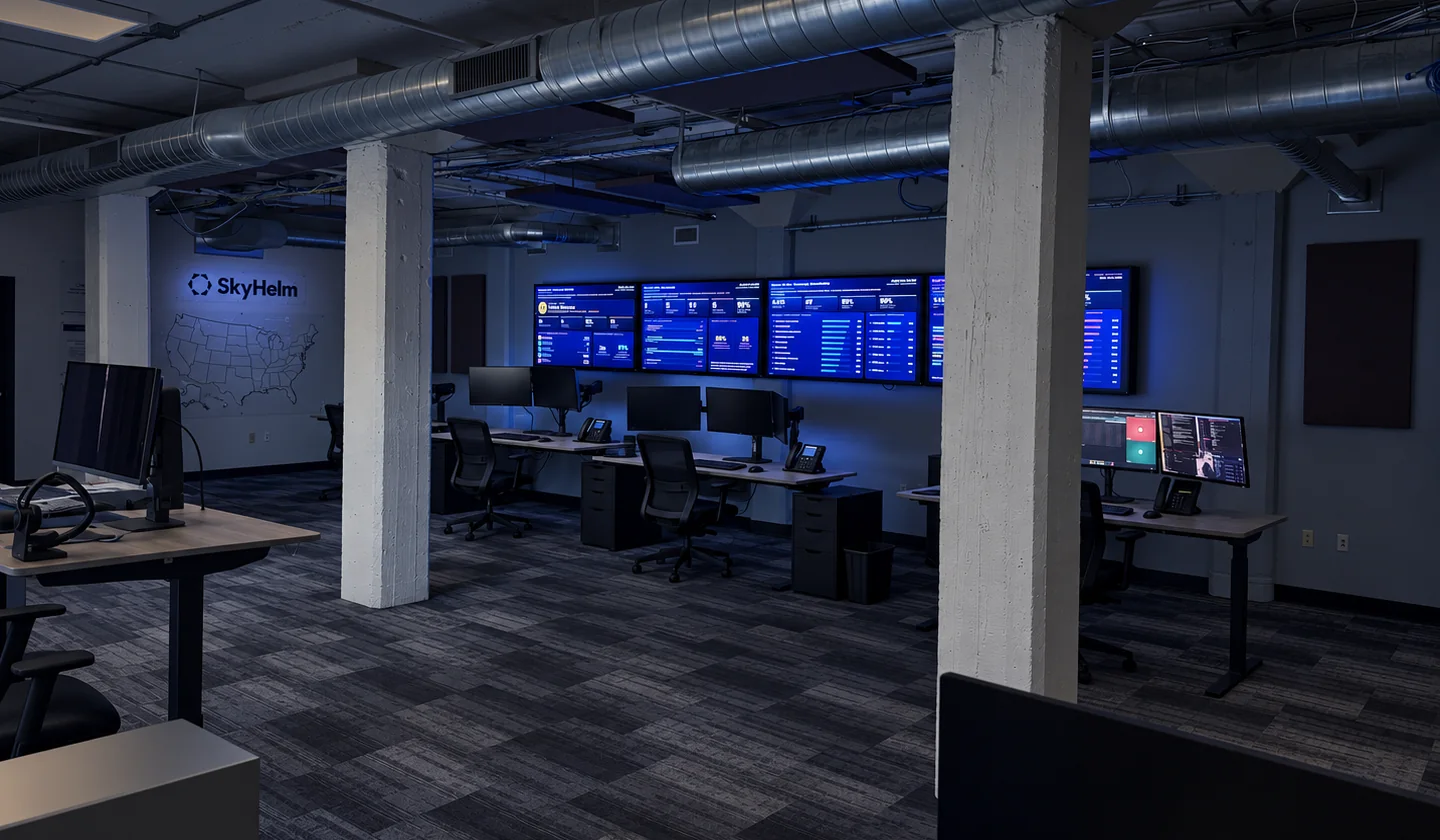
US-based SOC analysts keep eyes on it 24/7, so your team doesn't have to.
This is SkyHelm.
We protect America's Critical Infrastructure.
One platform. Total visibility.
Purpose-built for critical infrastructure. No more tab-switching. No more blind spots.
US-based analysts who know critical infrastructure networks.
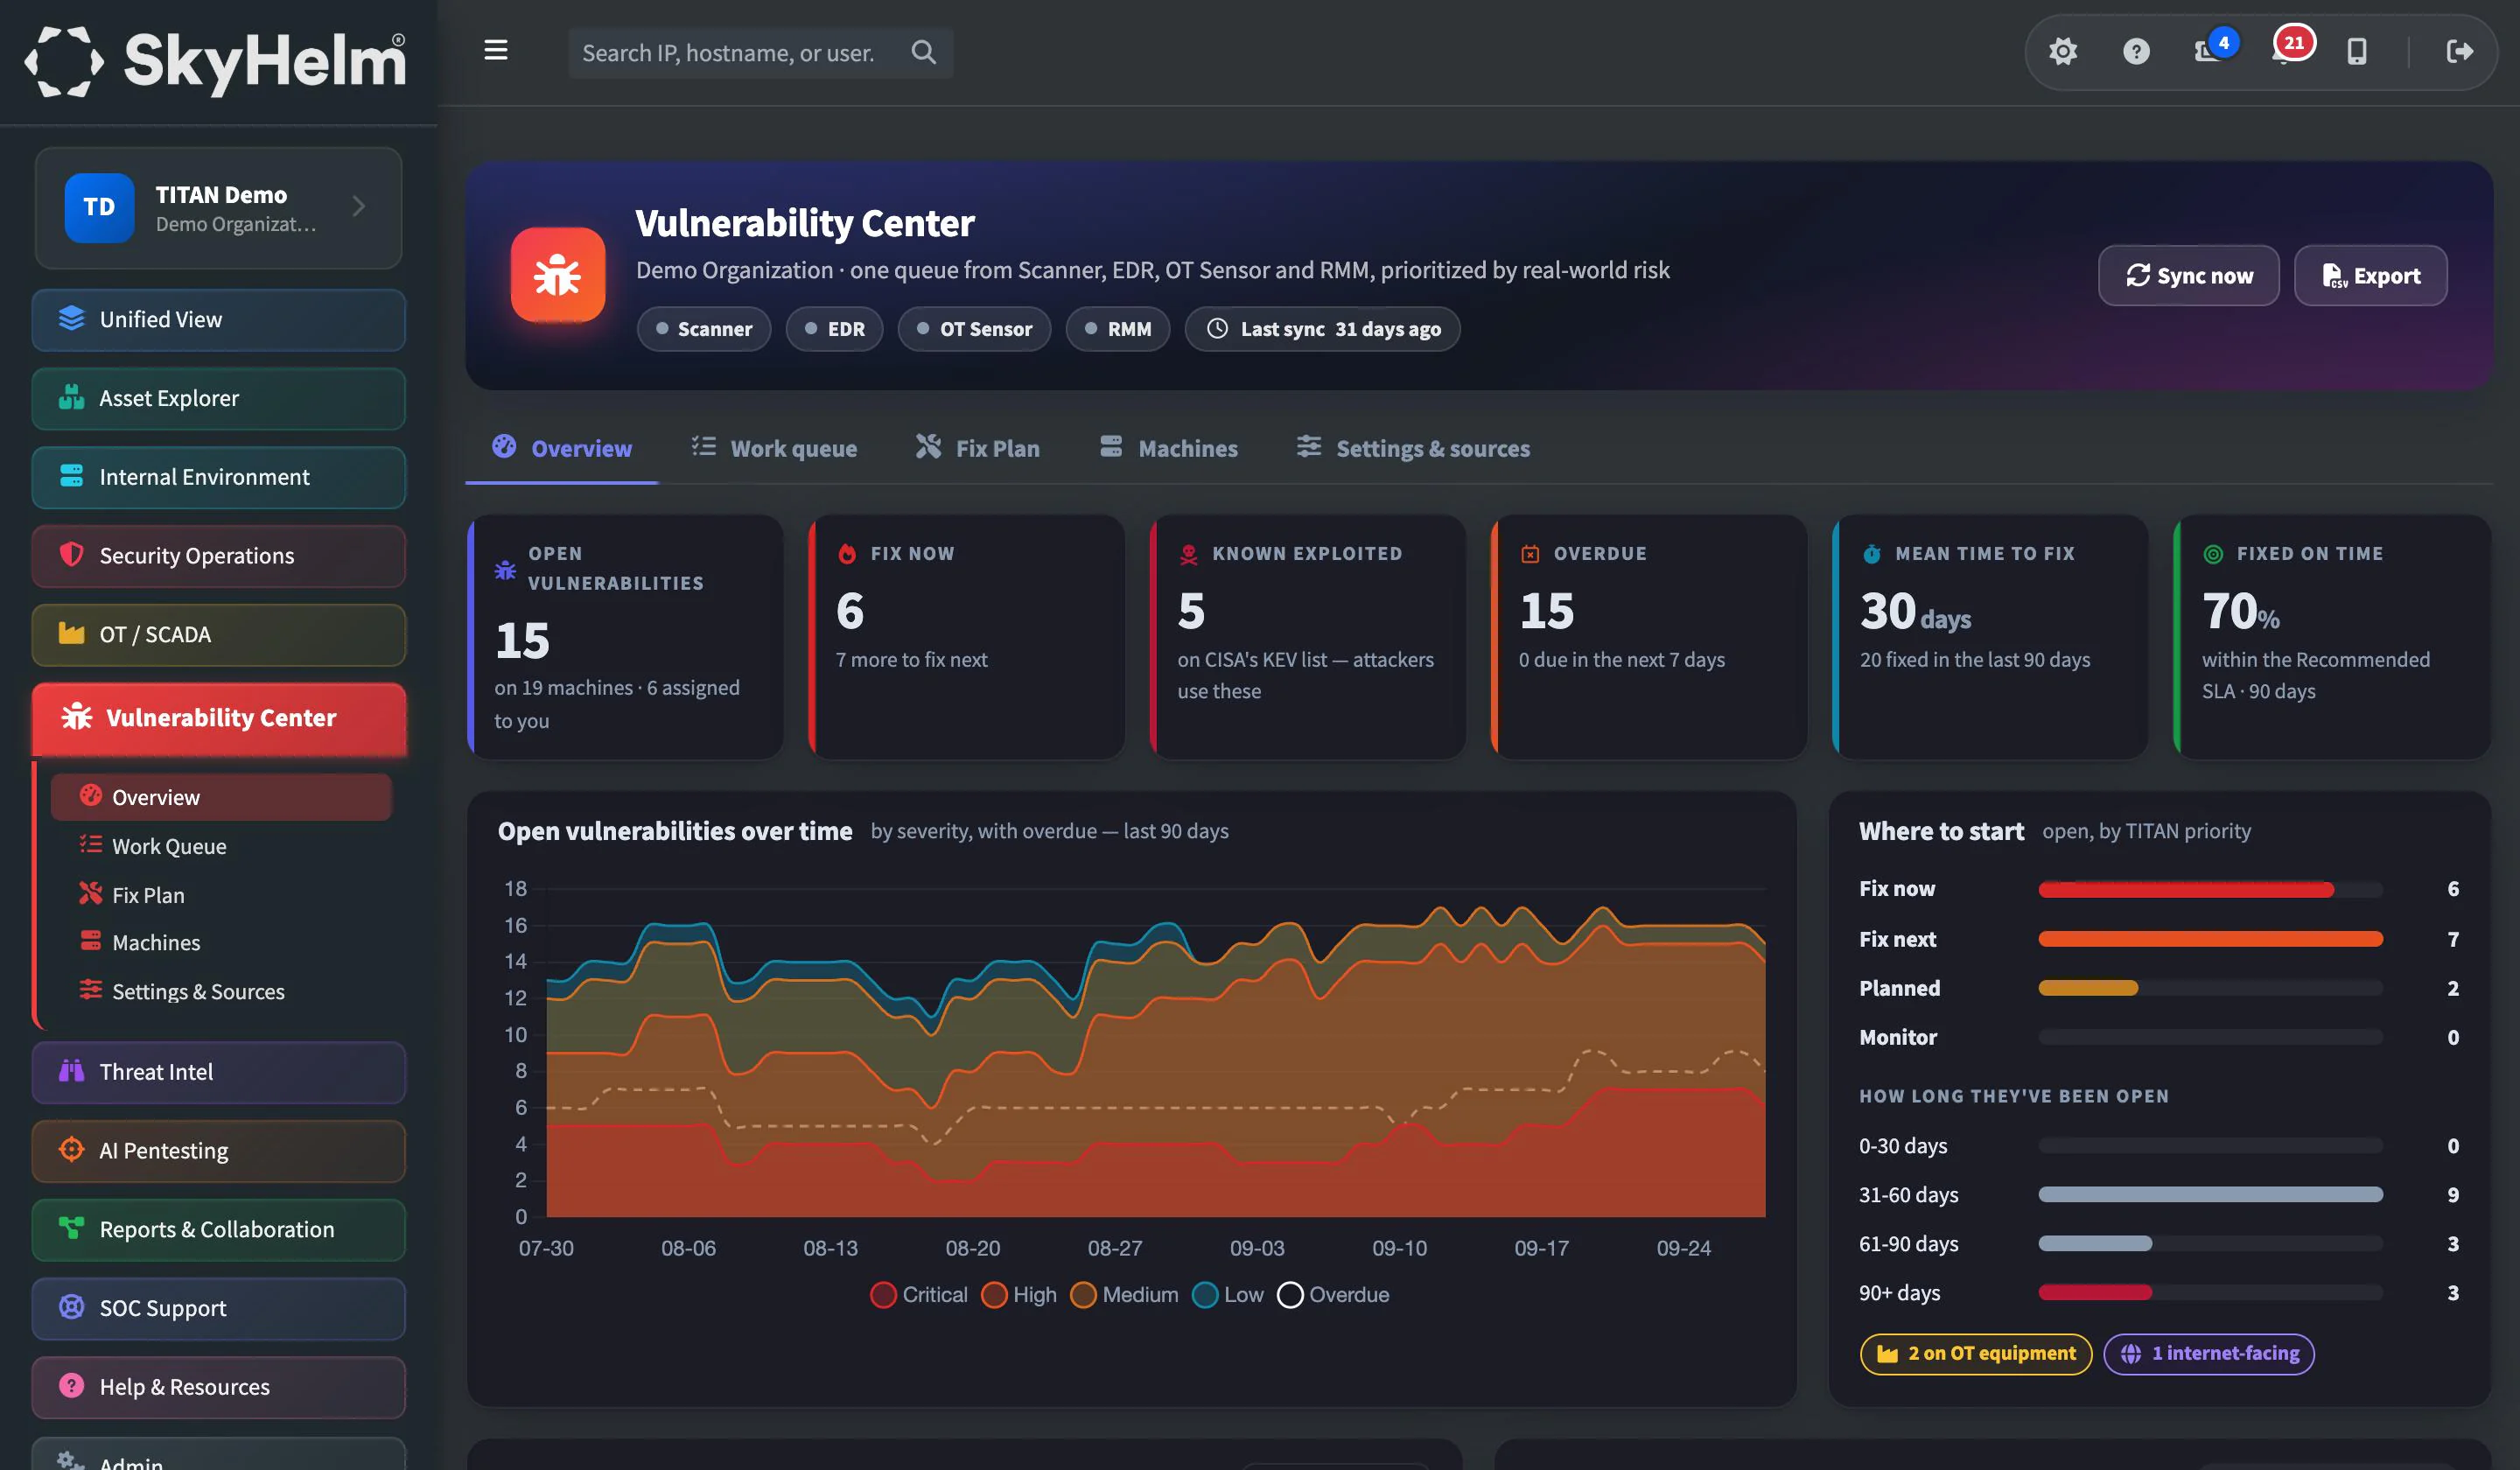
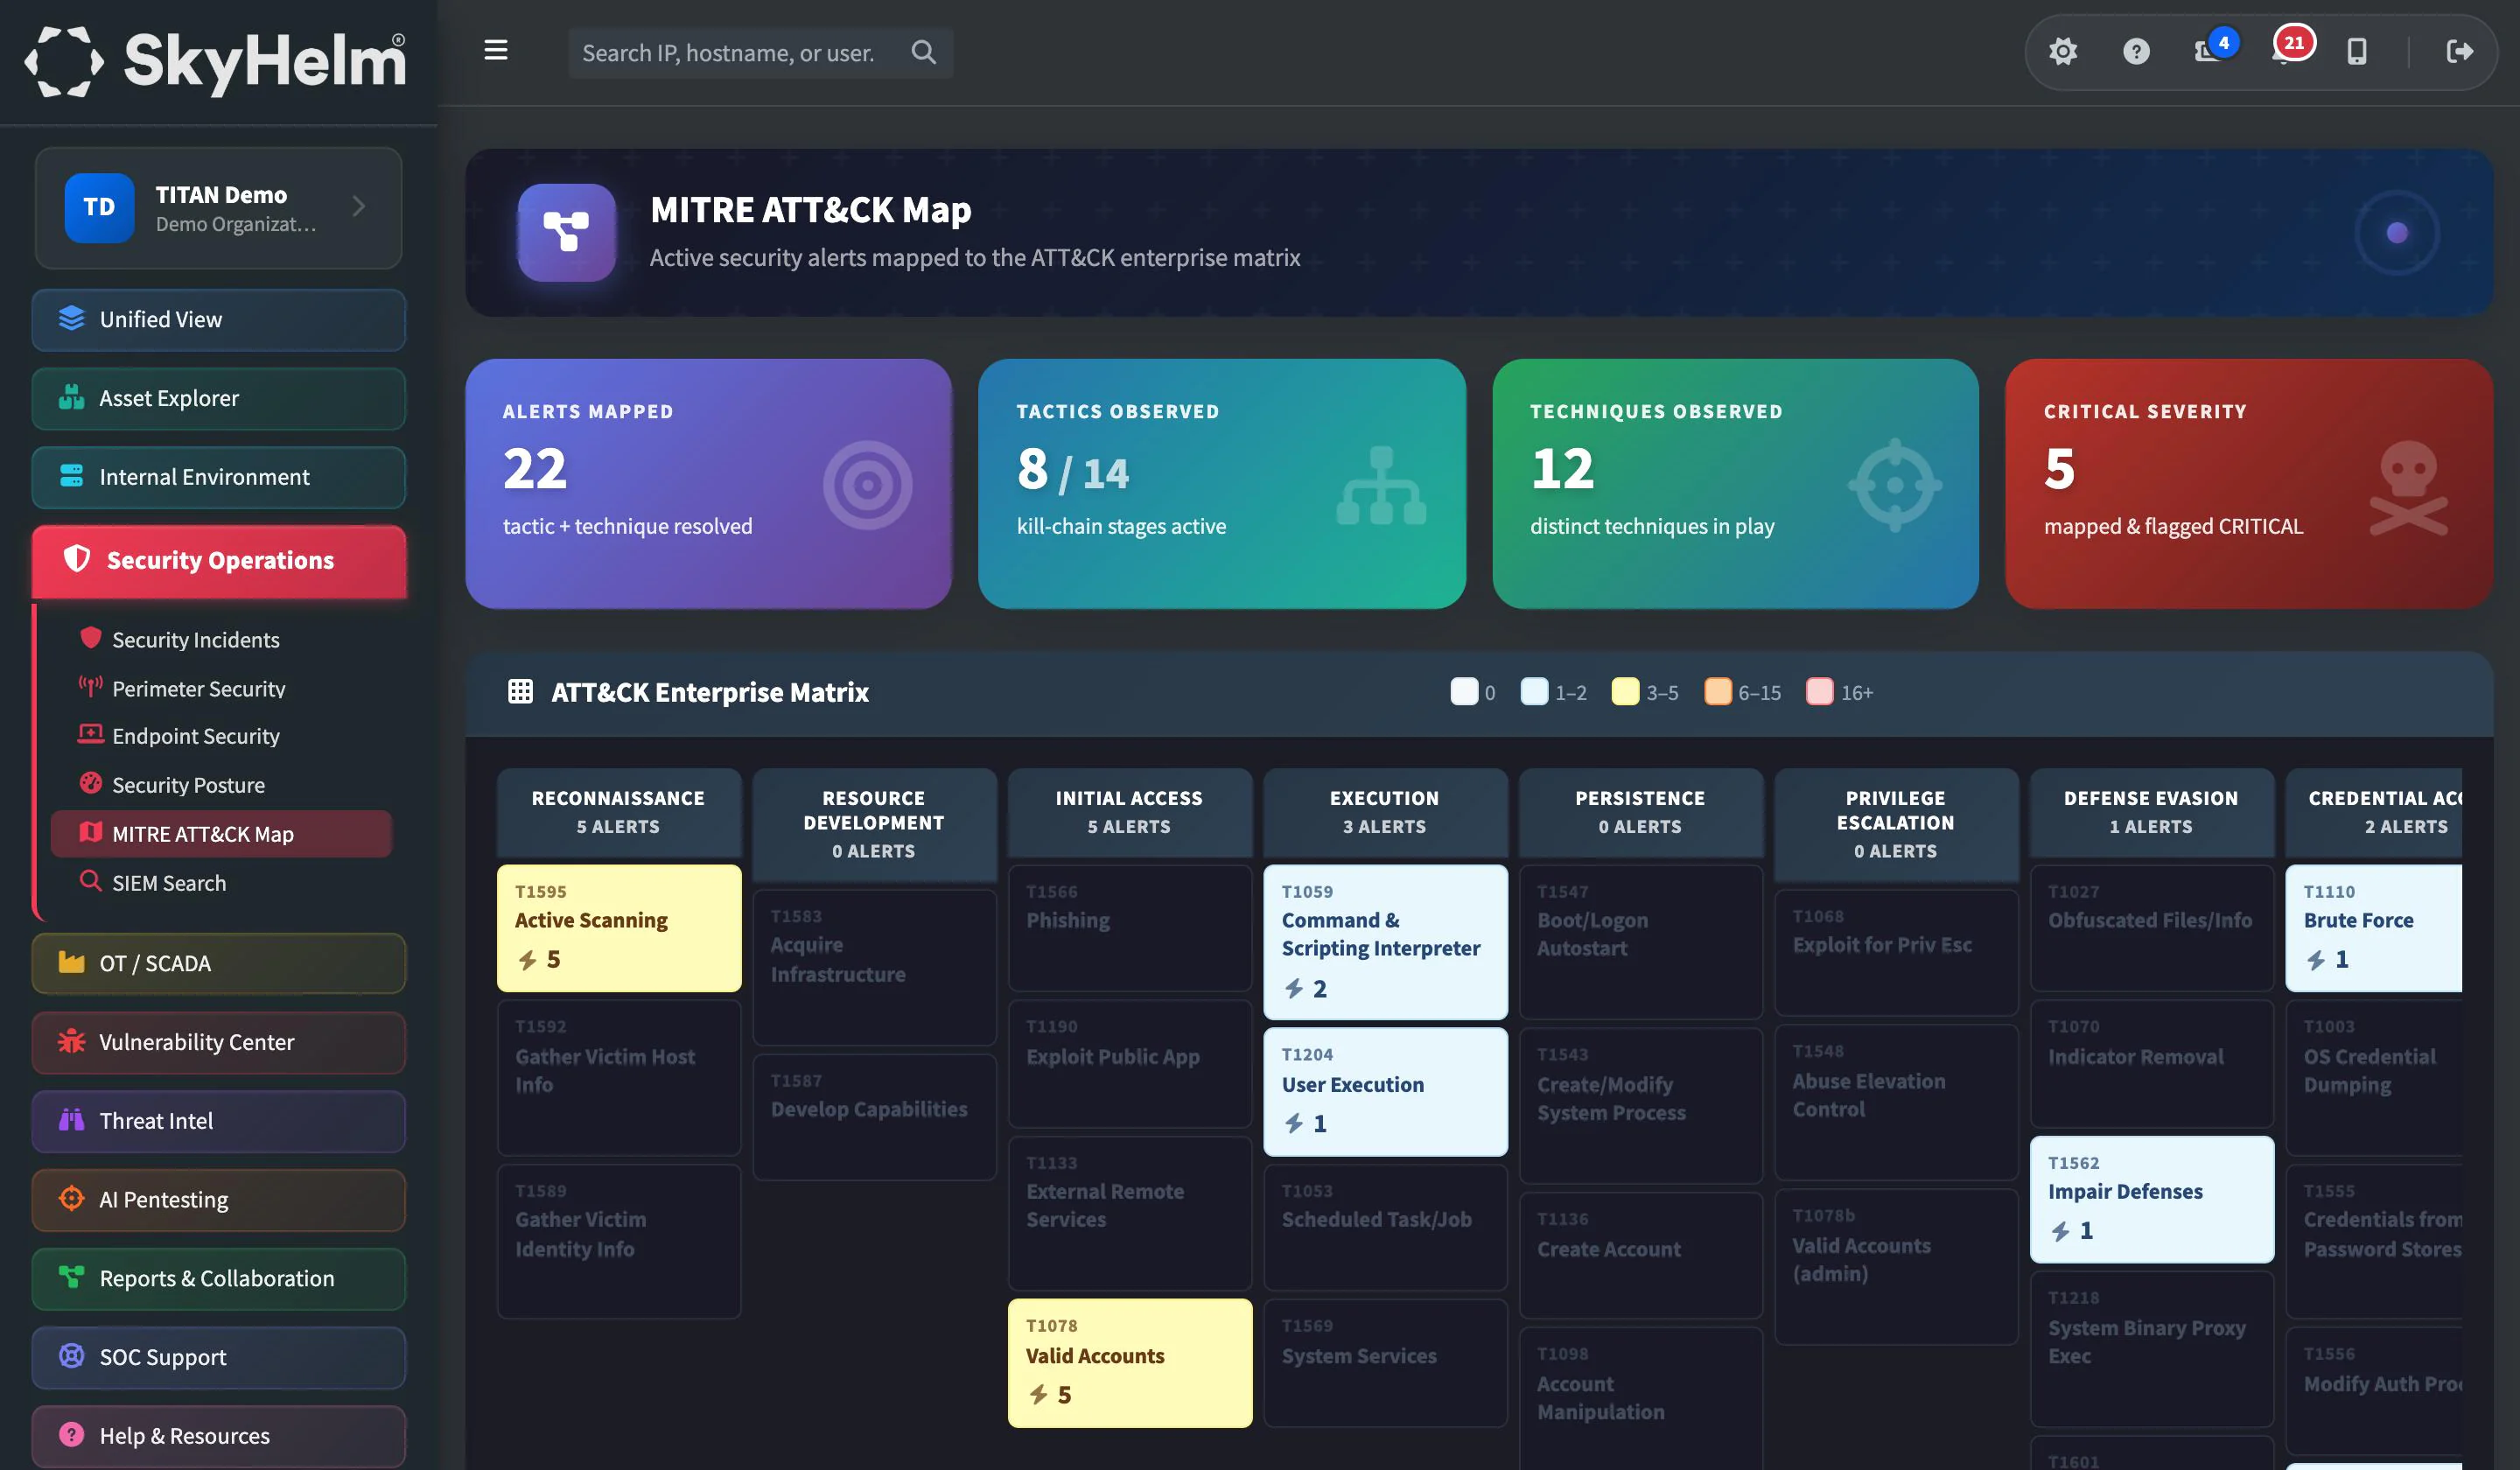
See the attack the way analysts do.
Every alert is placed on the attacker's playbook, so you know how far along a threat is at a glance.
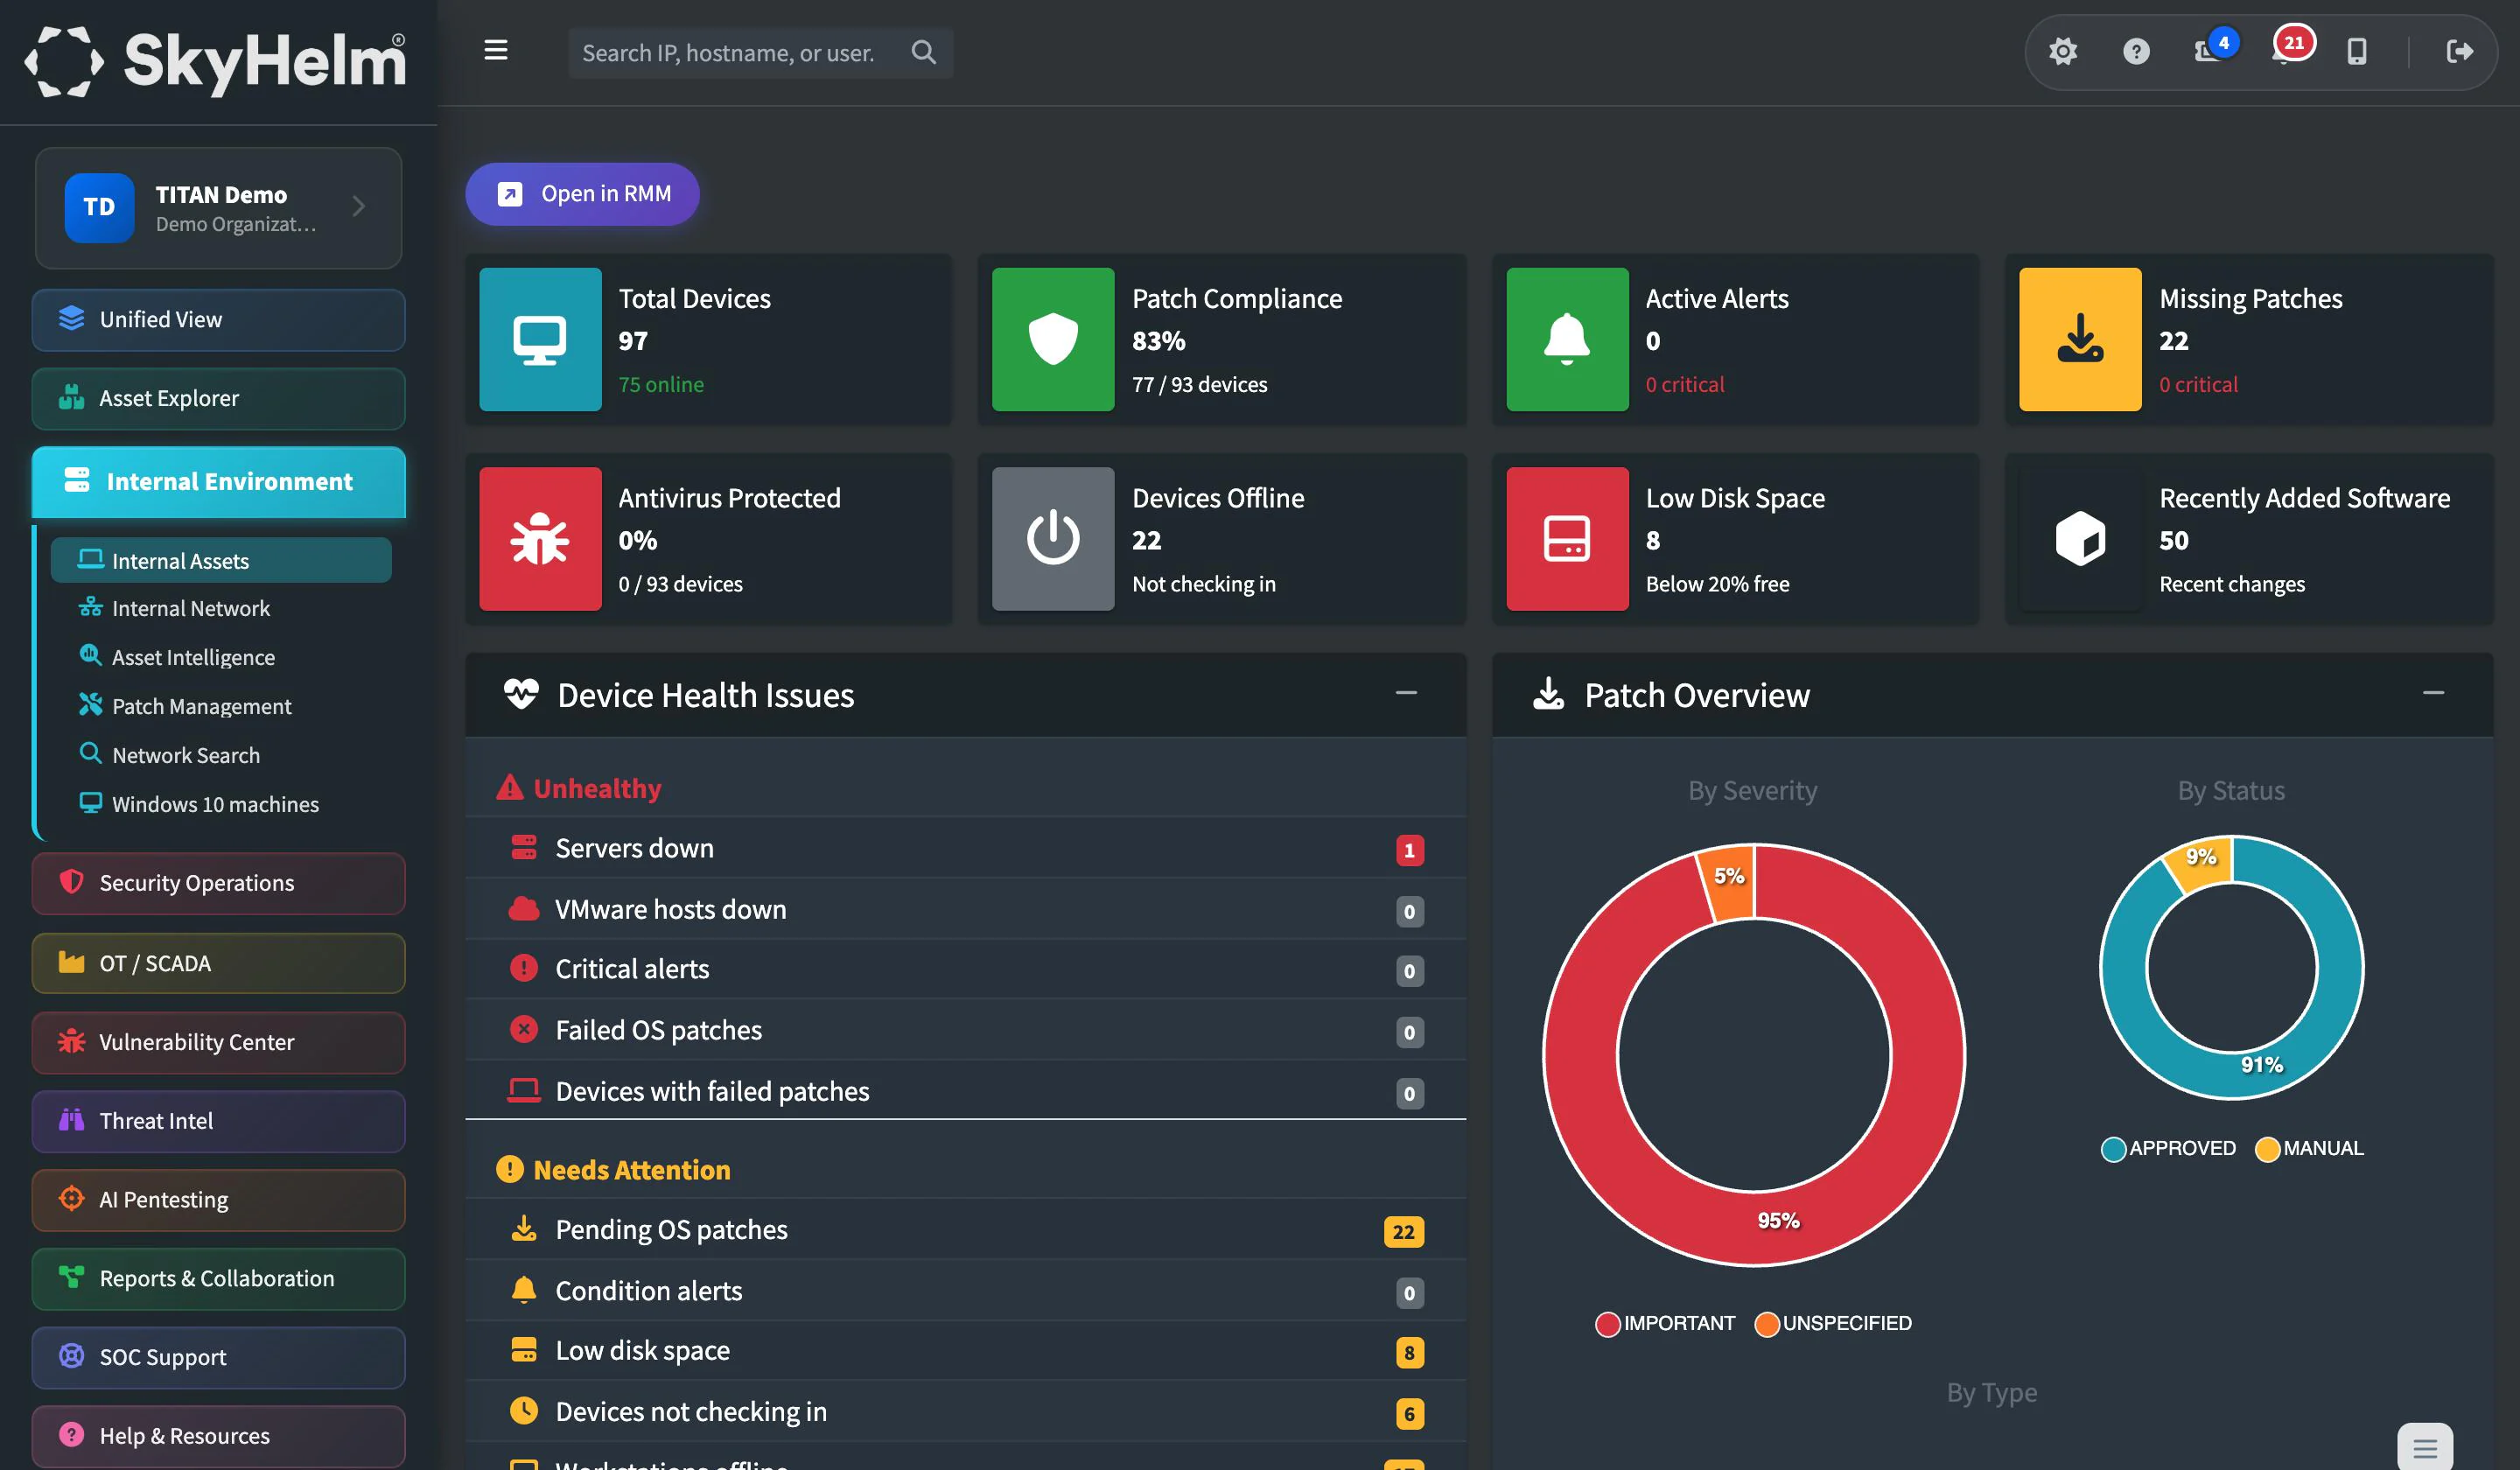
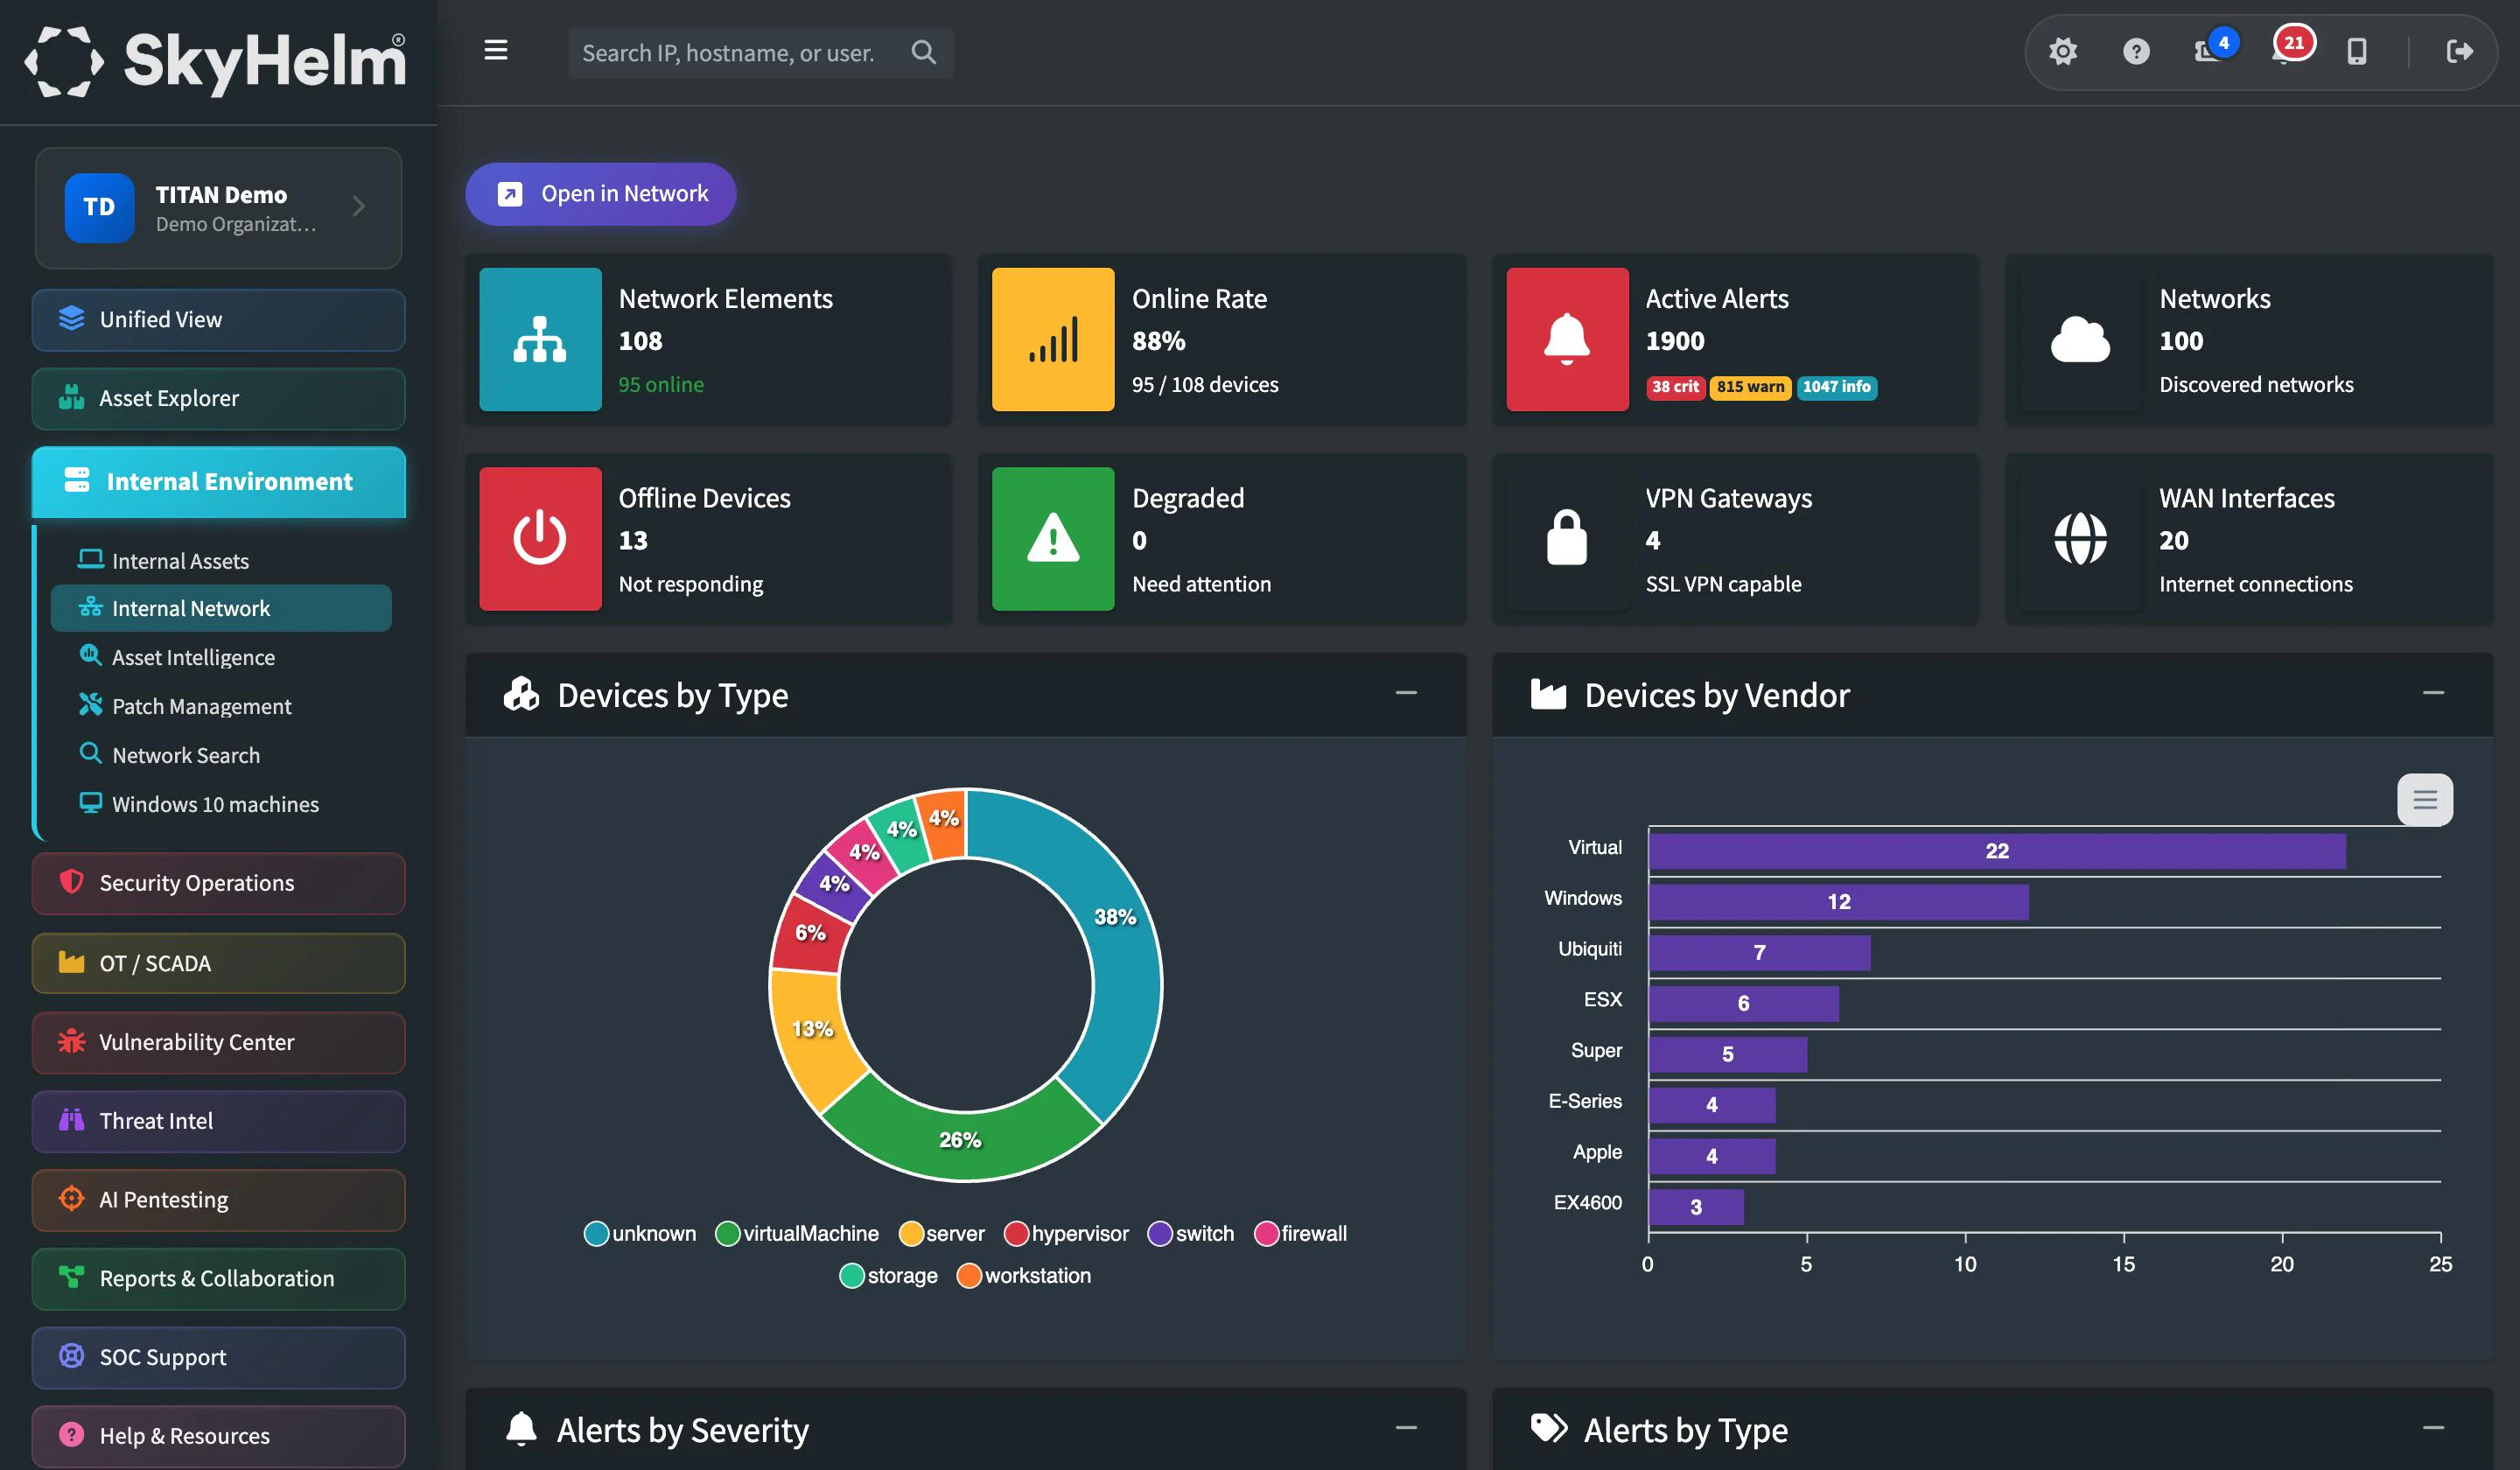
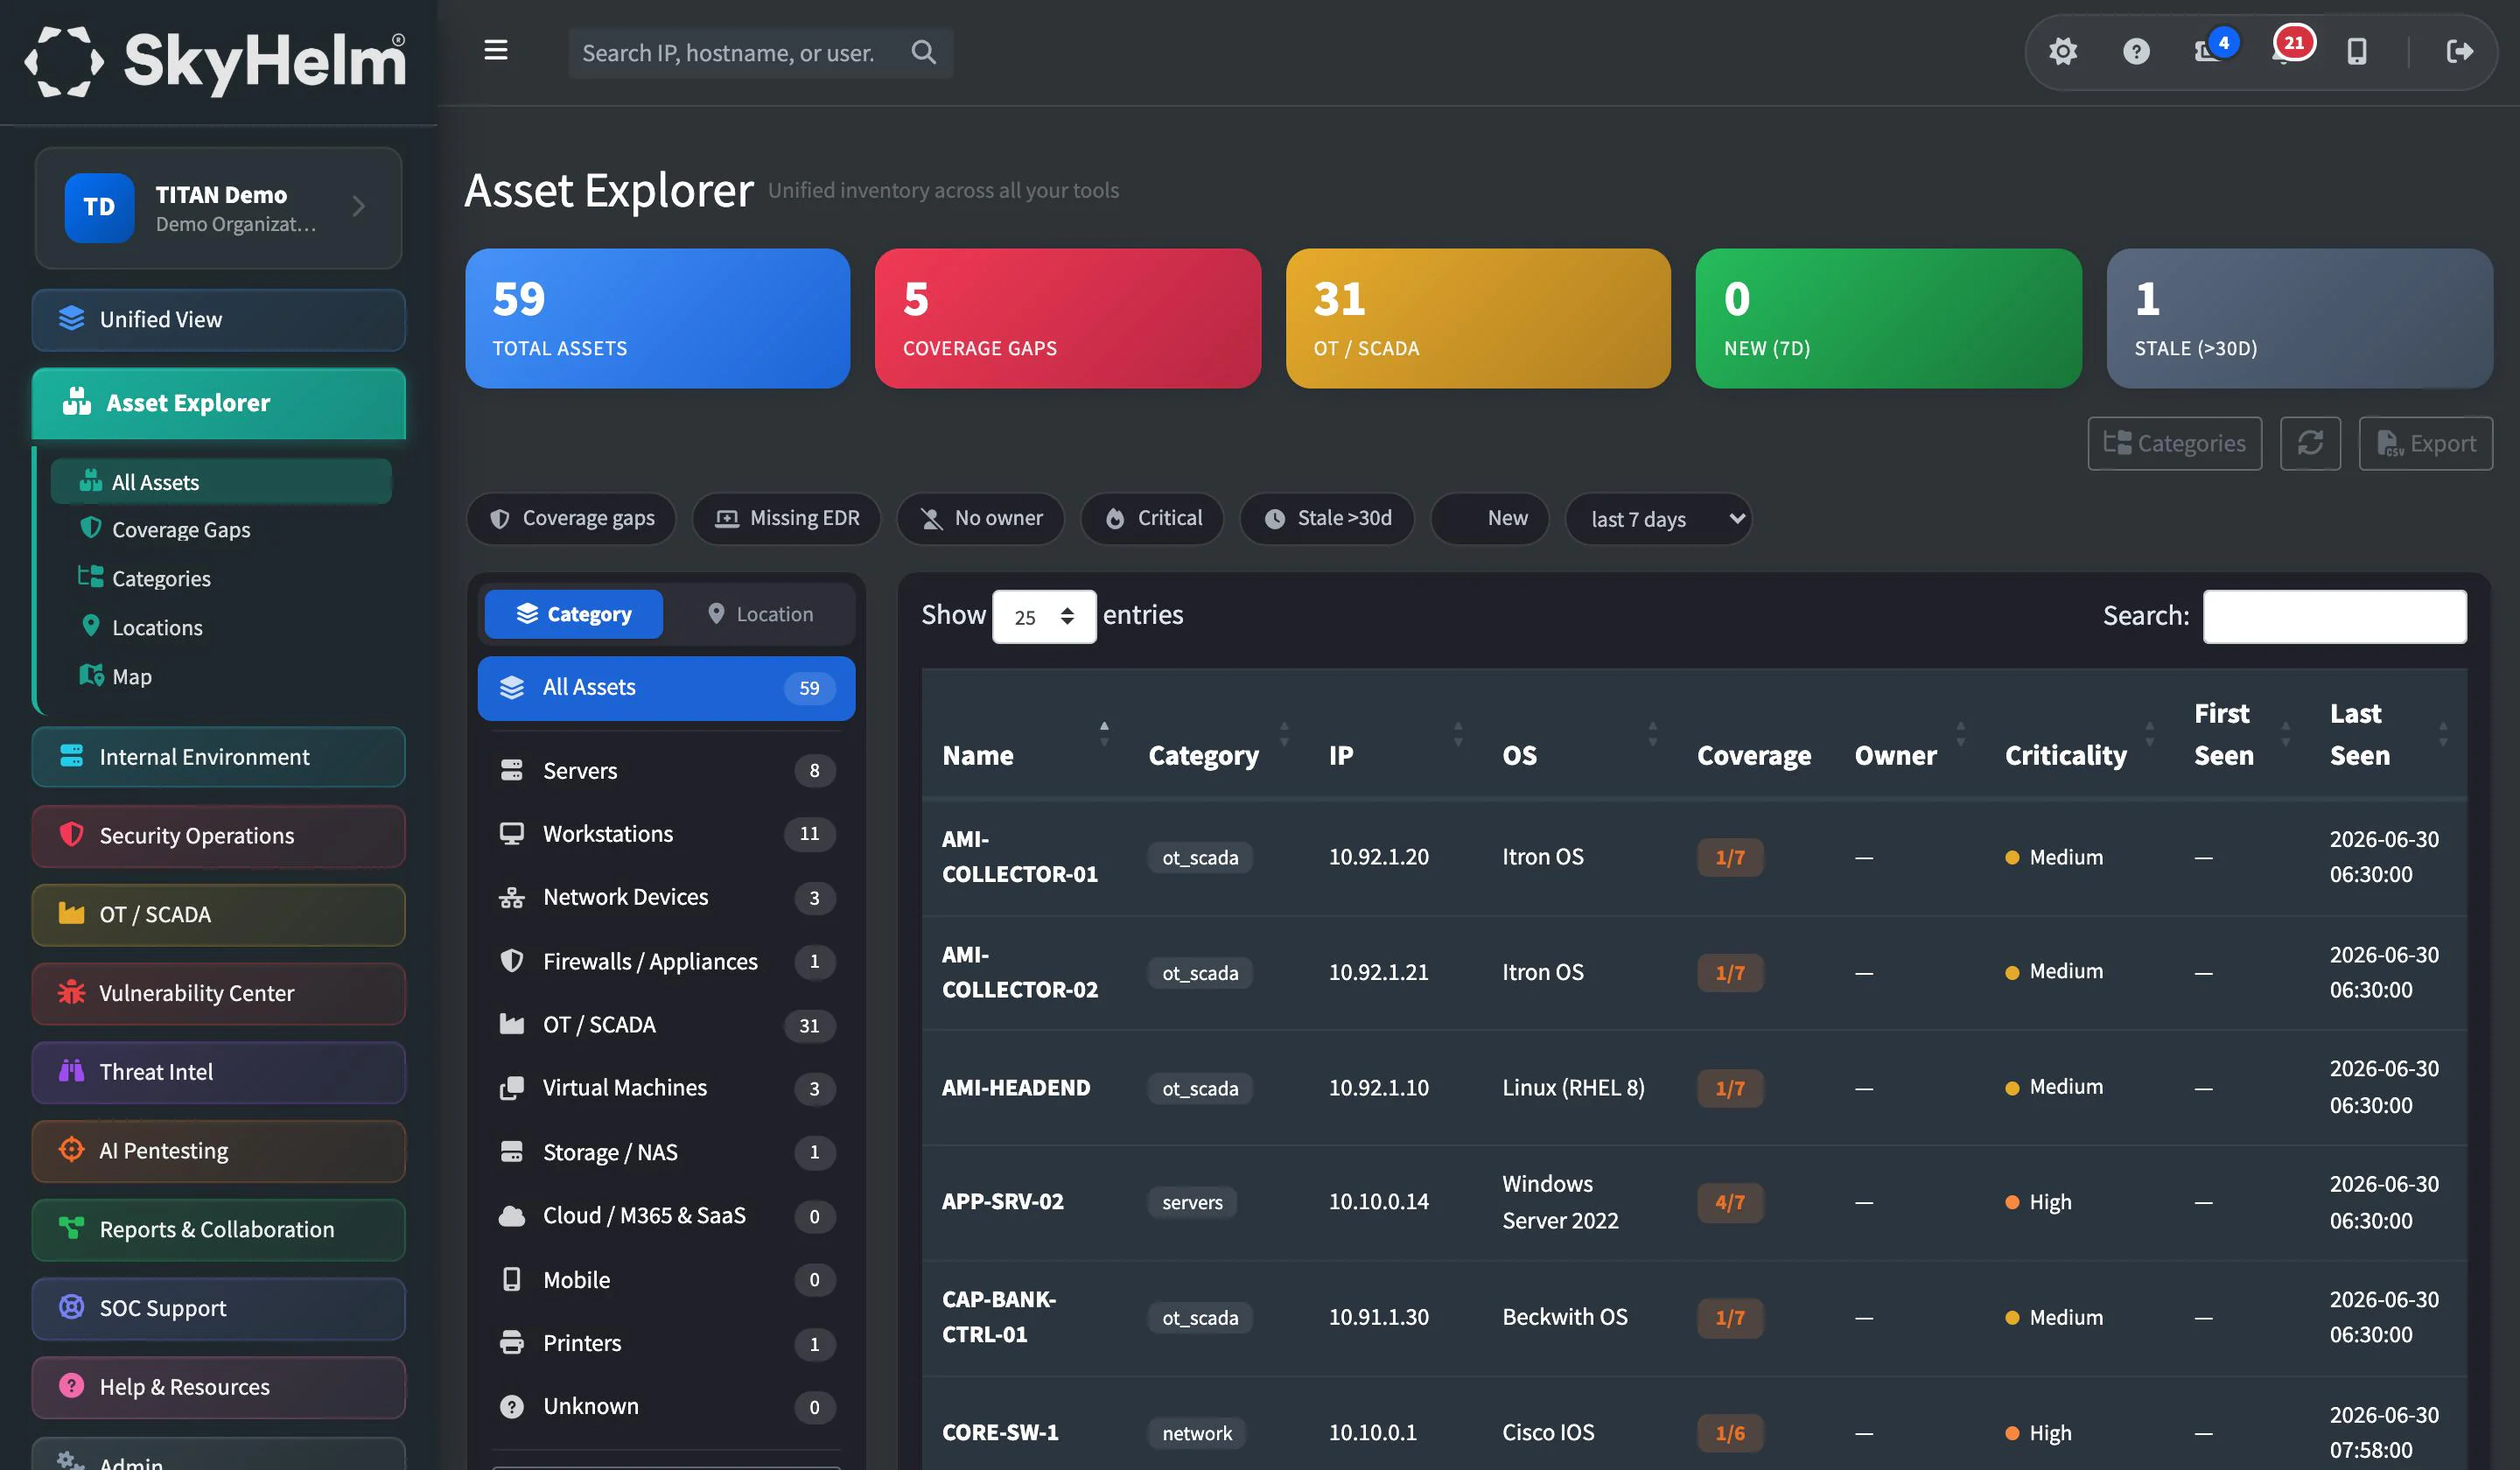
Every corner of your network.
Keep scrolling to turn through TITAN.
Your network never sleeps. Neither do we.
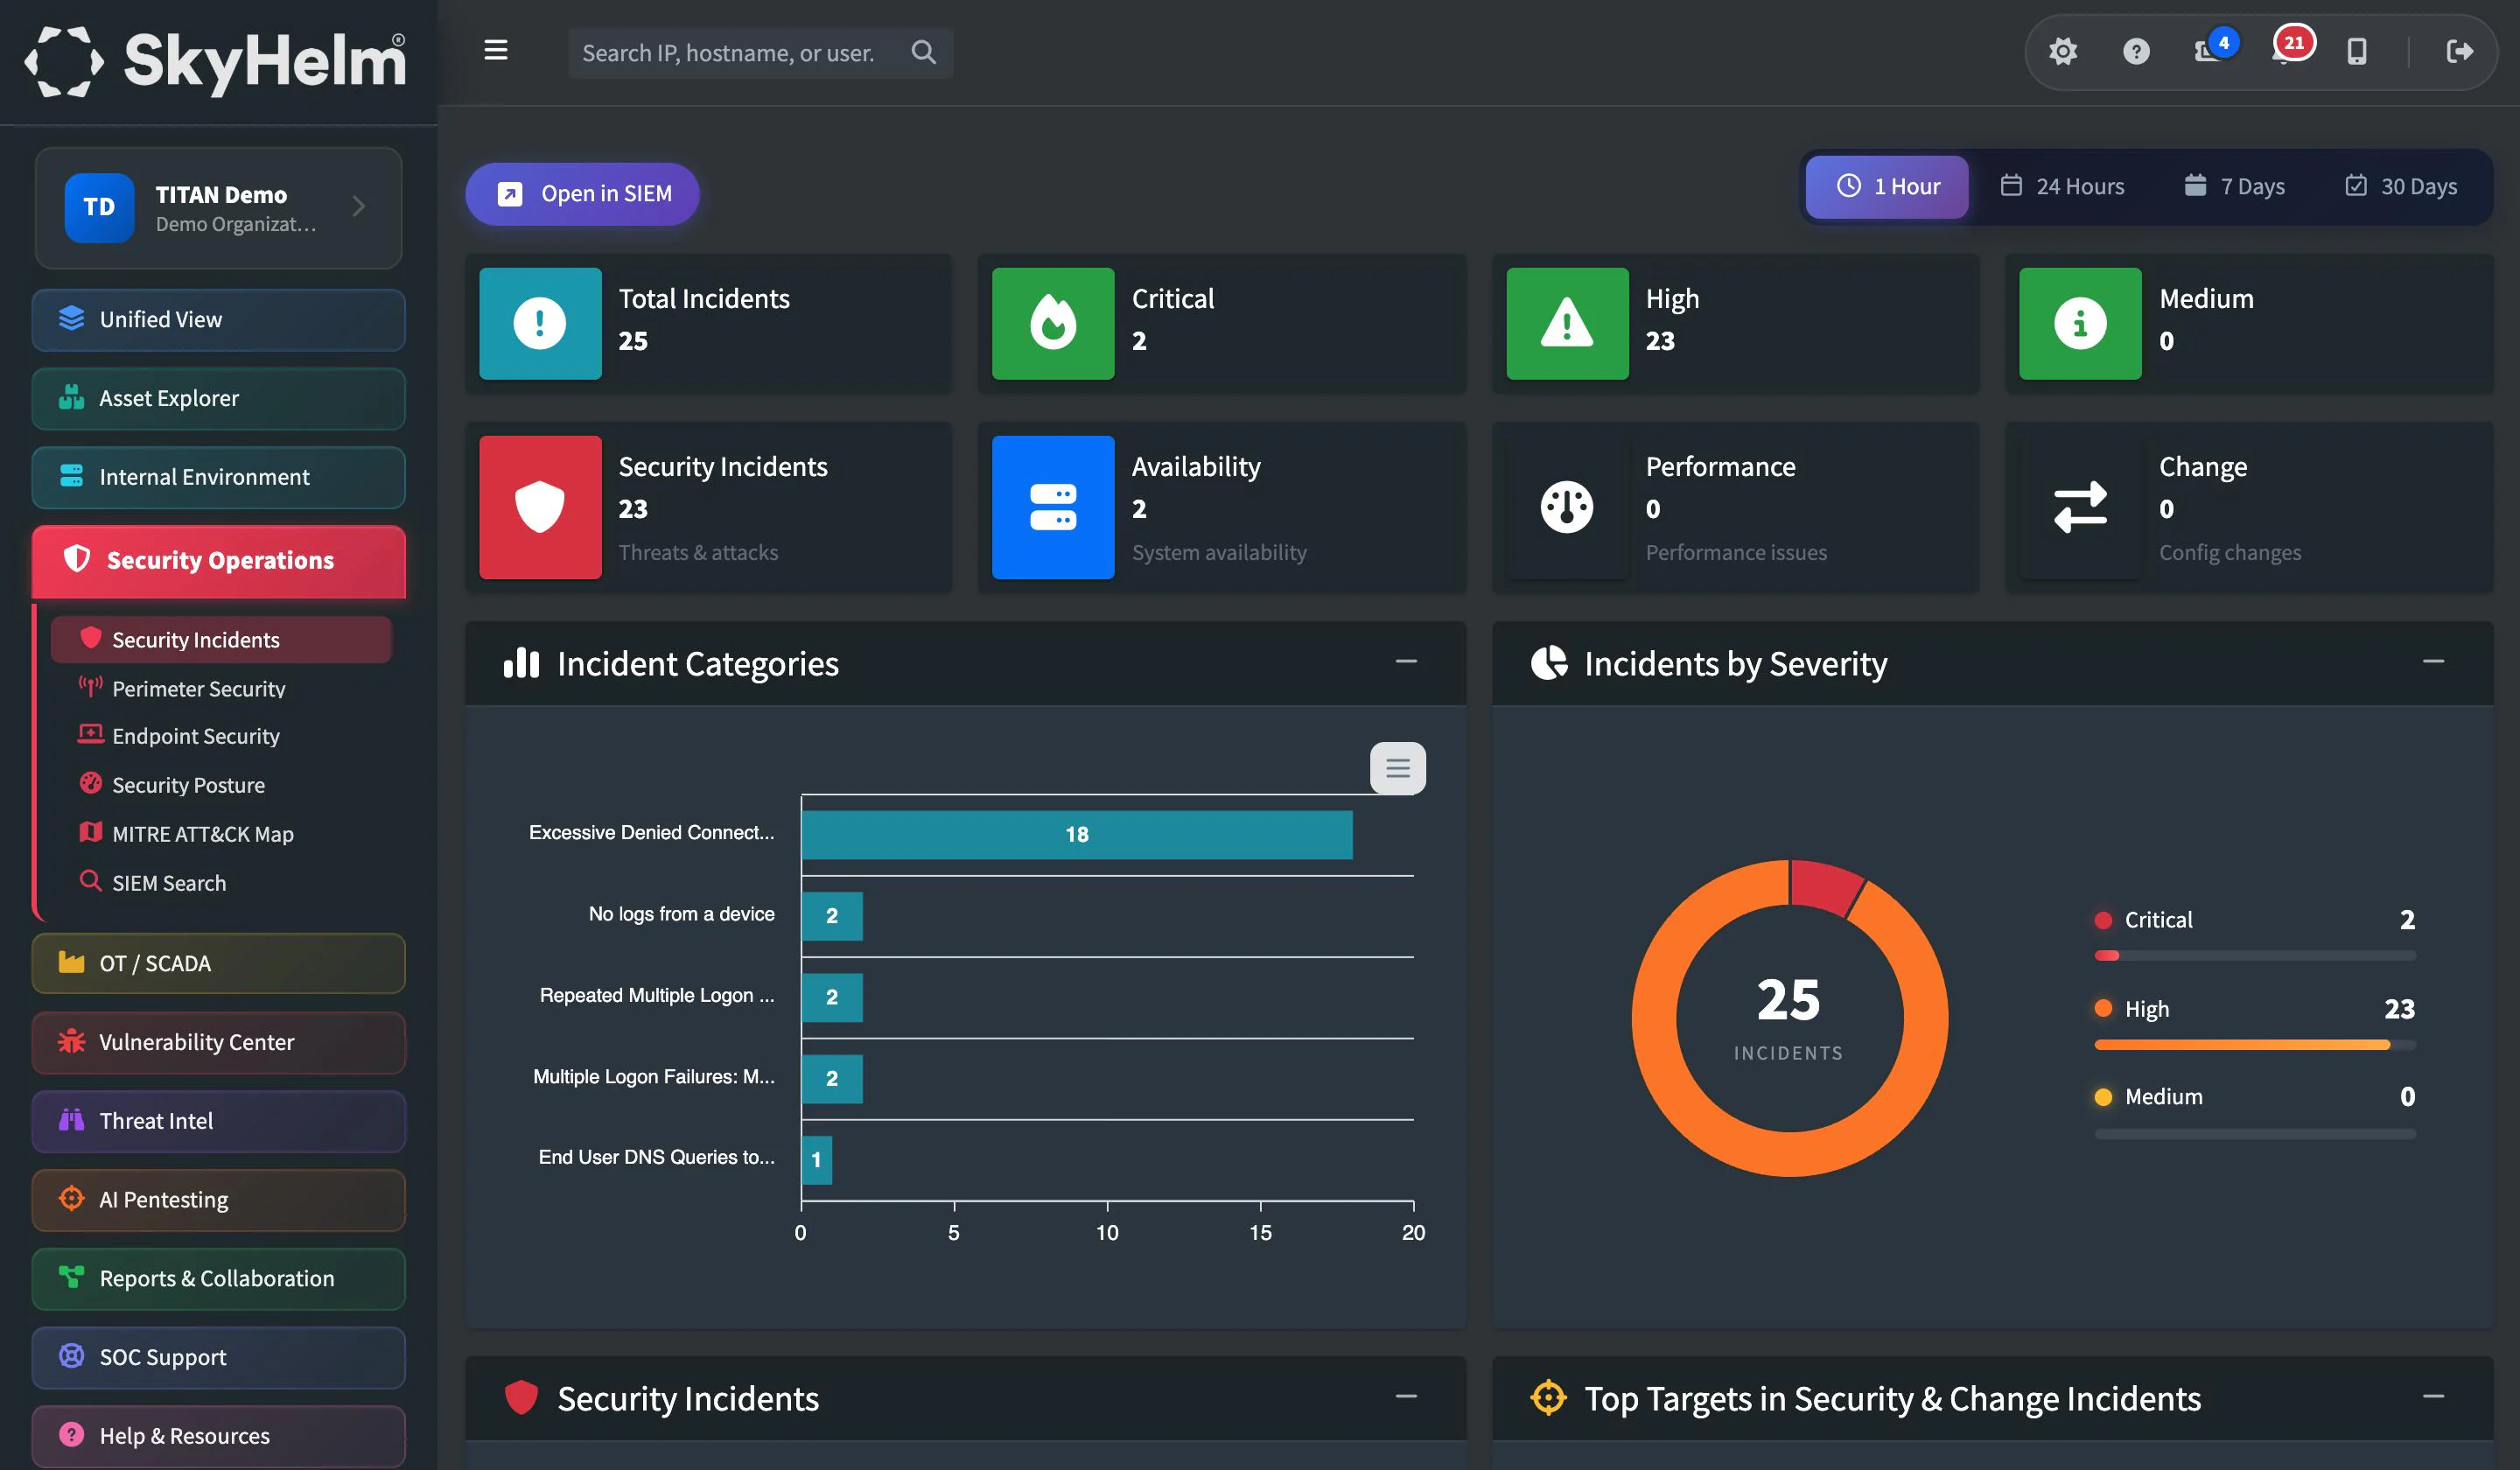
Our analysts triage alerts, investigate anomalies and escalate threats before they become incidents.
Every signal, one console.
Alerts from firewalls, endpoints, OT sensors and logs land in one queue, correlated and enriched before an analyst ever opens them.
Analysts who know critical infrastructure.
A US-based SOC analyst pulls the logs, checks the asset and its history, and builds context with what normal looks like on your network.
Contained within the response window.
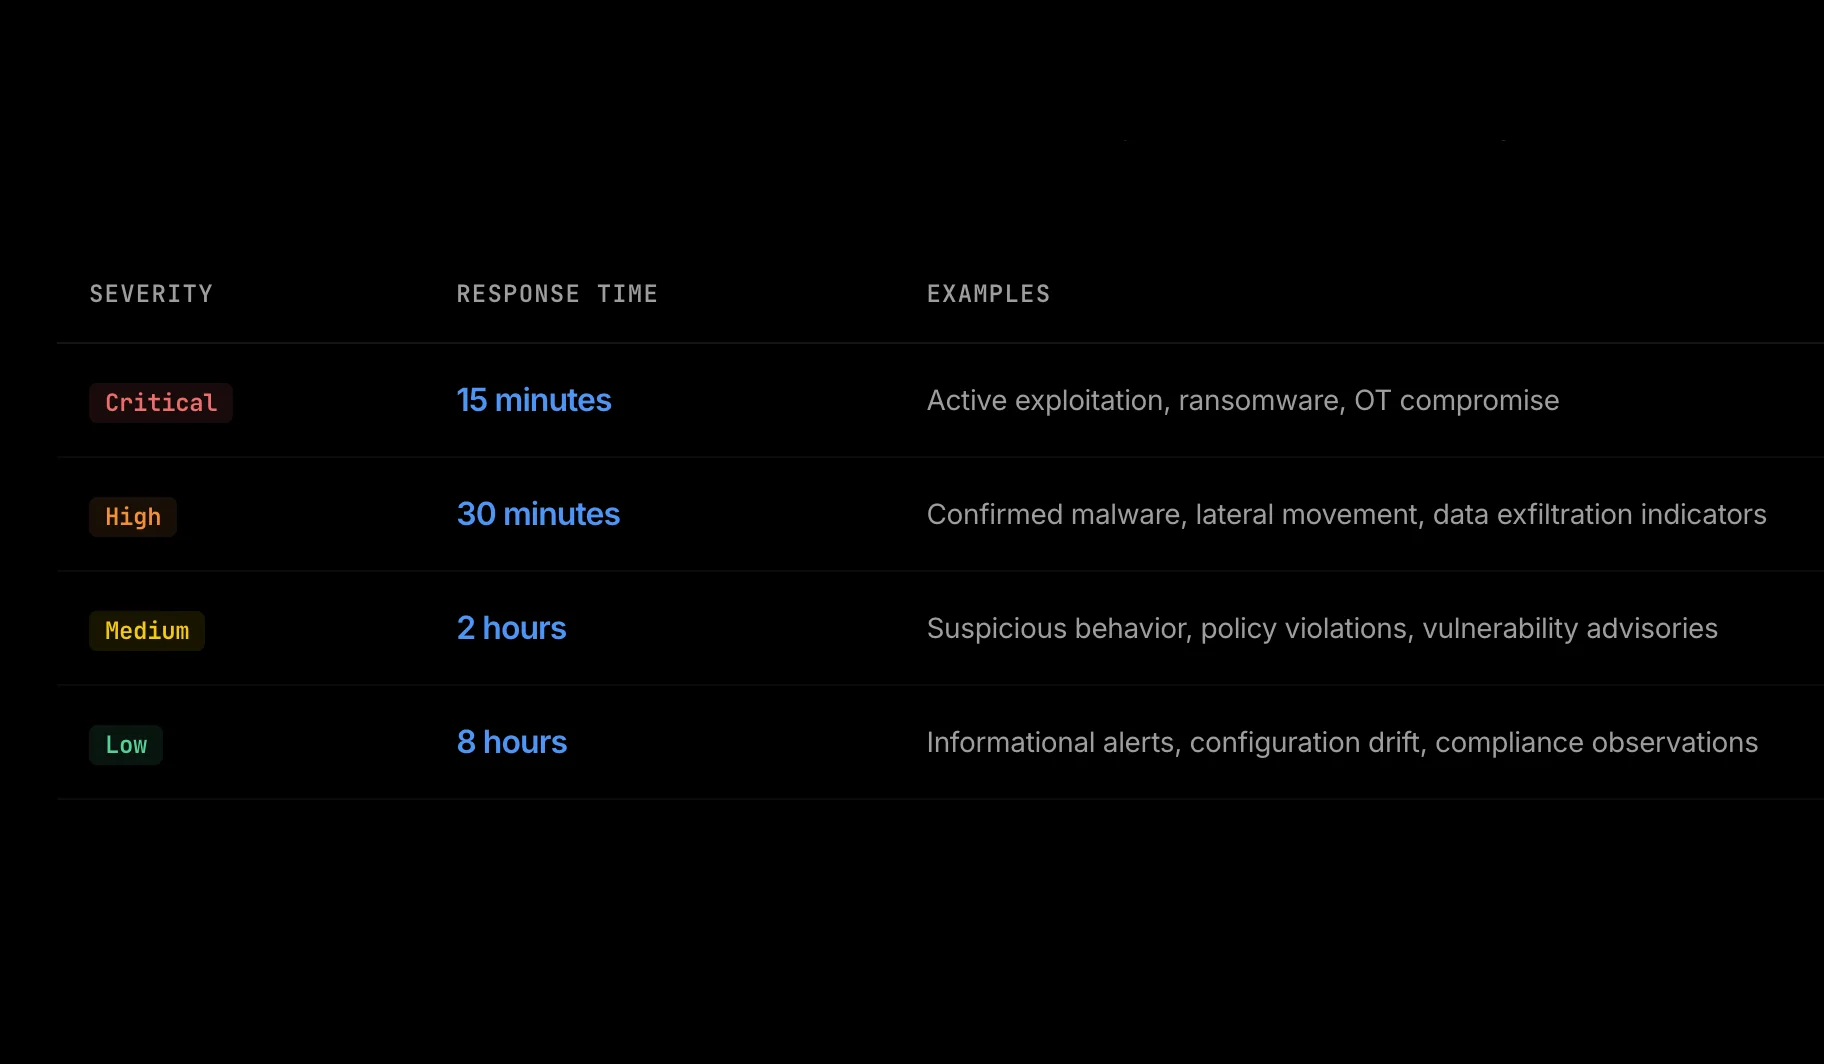
For critical and high-severity threats, endpoints are isolated, accounts locked and malicious IPs blocked, with a 15-minute critical alert response SLA.
Closed, documented, audit-ready.
Your team gets the full story and the fix that closes the hole, and every action is timestamped for your audit and compliance evidence.
Learn more ›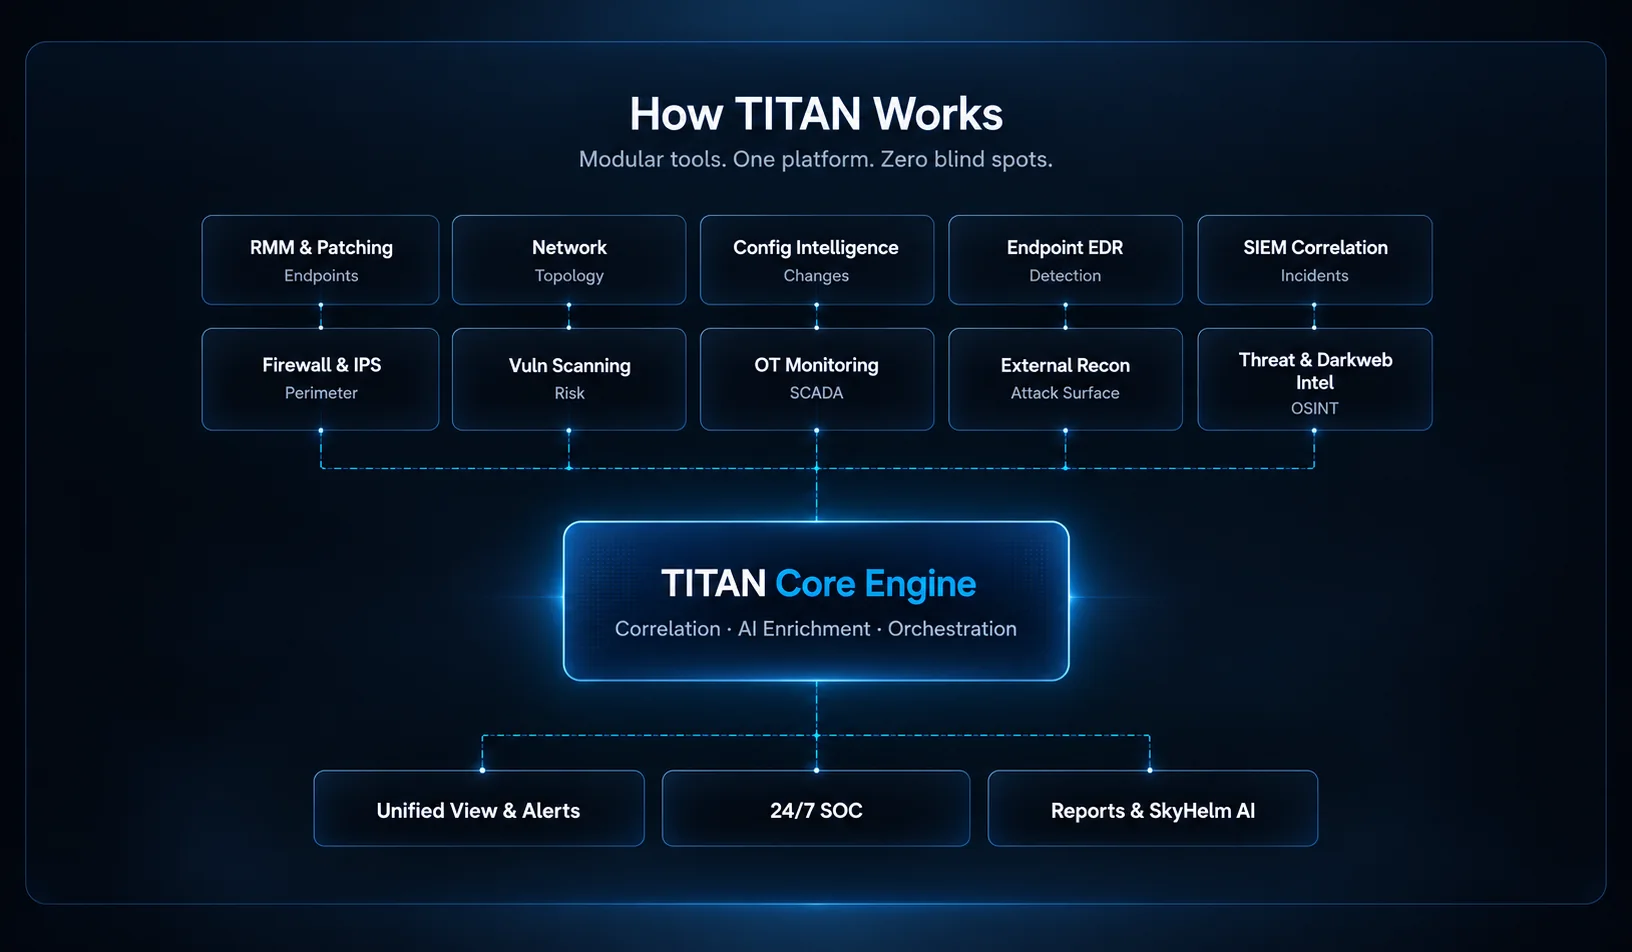
Every signal, one console.
Alerts from firewalls, endpoints, OT sensors and logs land in one queue, correlated and enriched before an analyst ever opens them.
Analysts who know critical infrastructure.
A US-based SOC analyst pulls the logs, checks the asset and its history, and builds context with what normal looks like on your network.
Contained within the response window.
For critical and high-severity threats, endpoints are isolated, accounts locked and malicious IPs blocked, with a 15-minute critical alert response SLA.
Closed, documented, audit-ready.
Your team gets the full story and the fix that closes the hole, and every action is timestamped for your audit and compliance evidence.
Learn more ›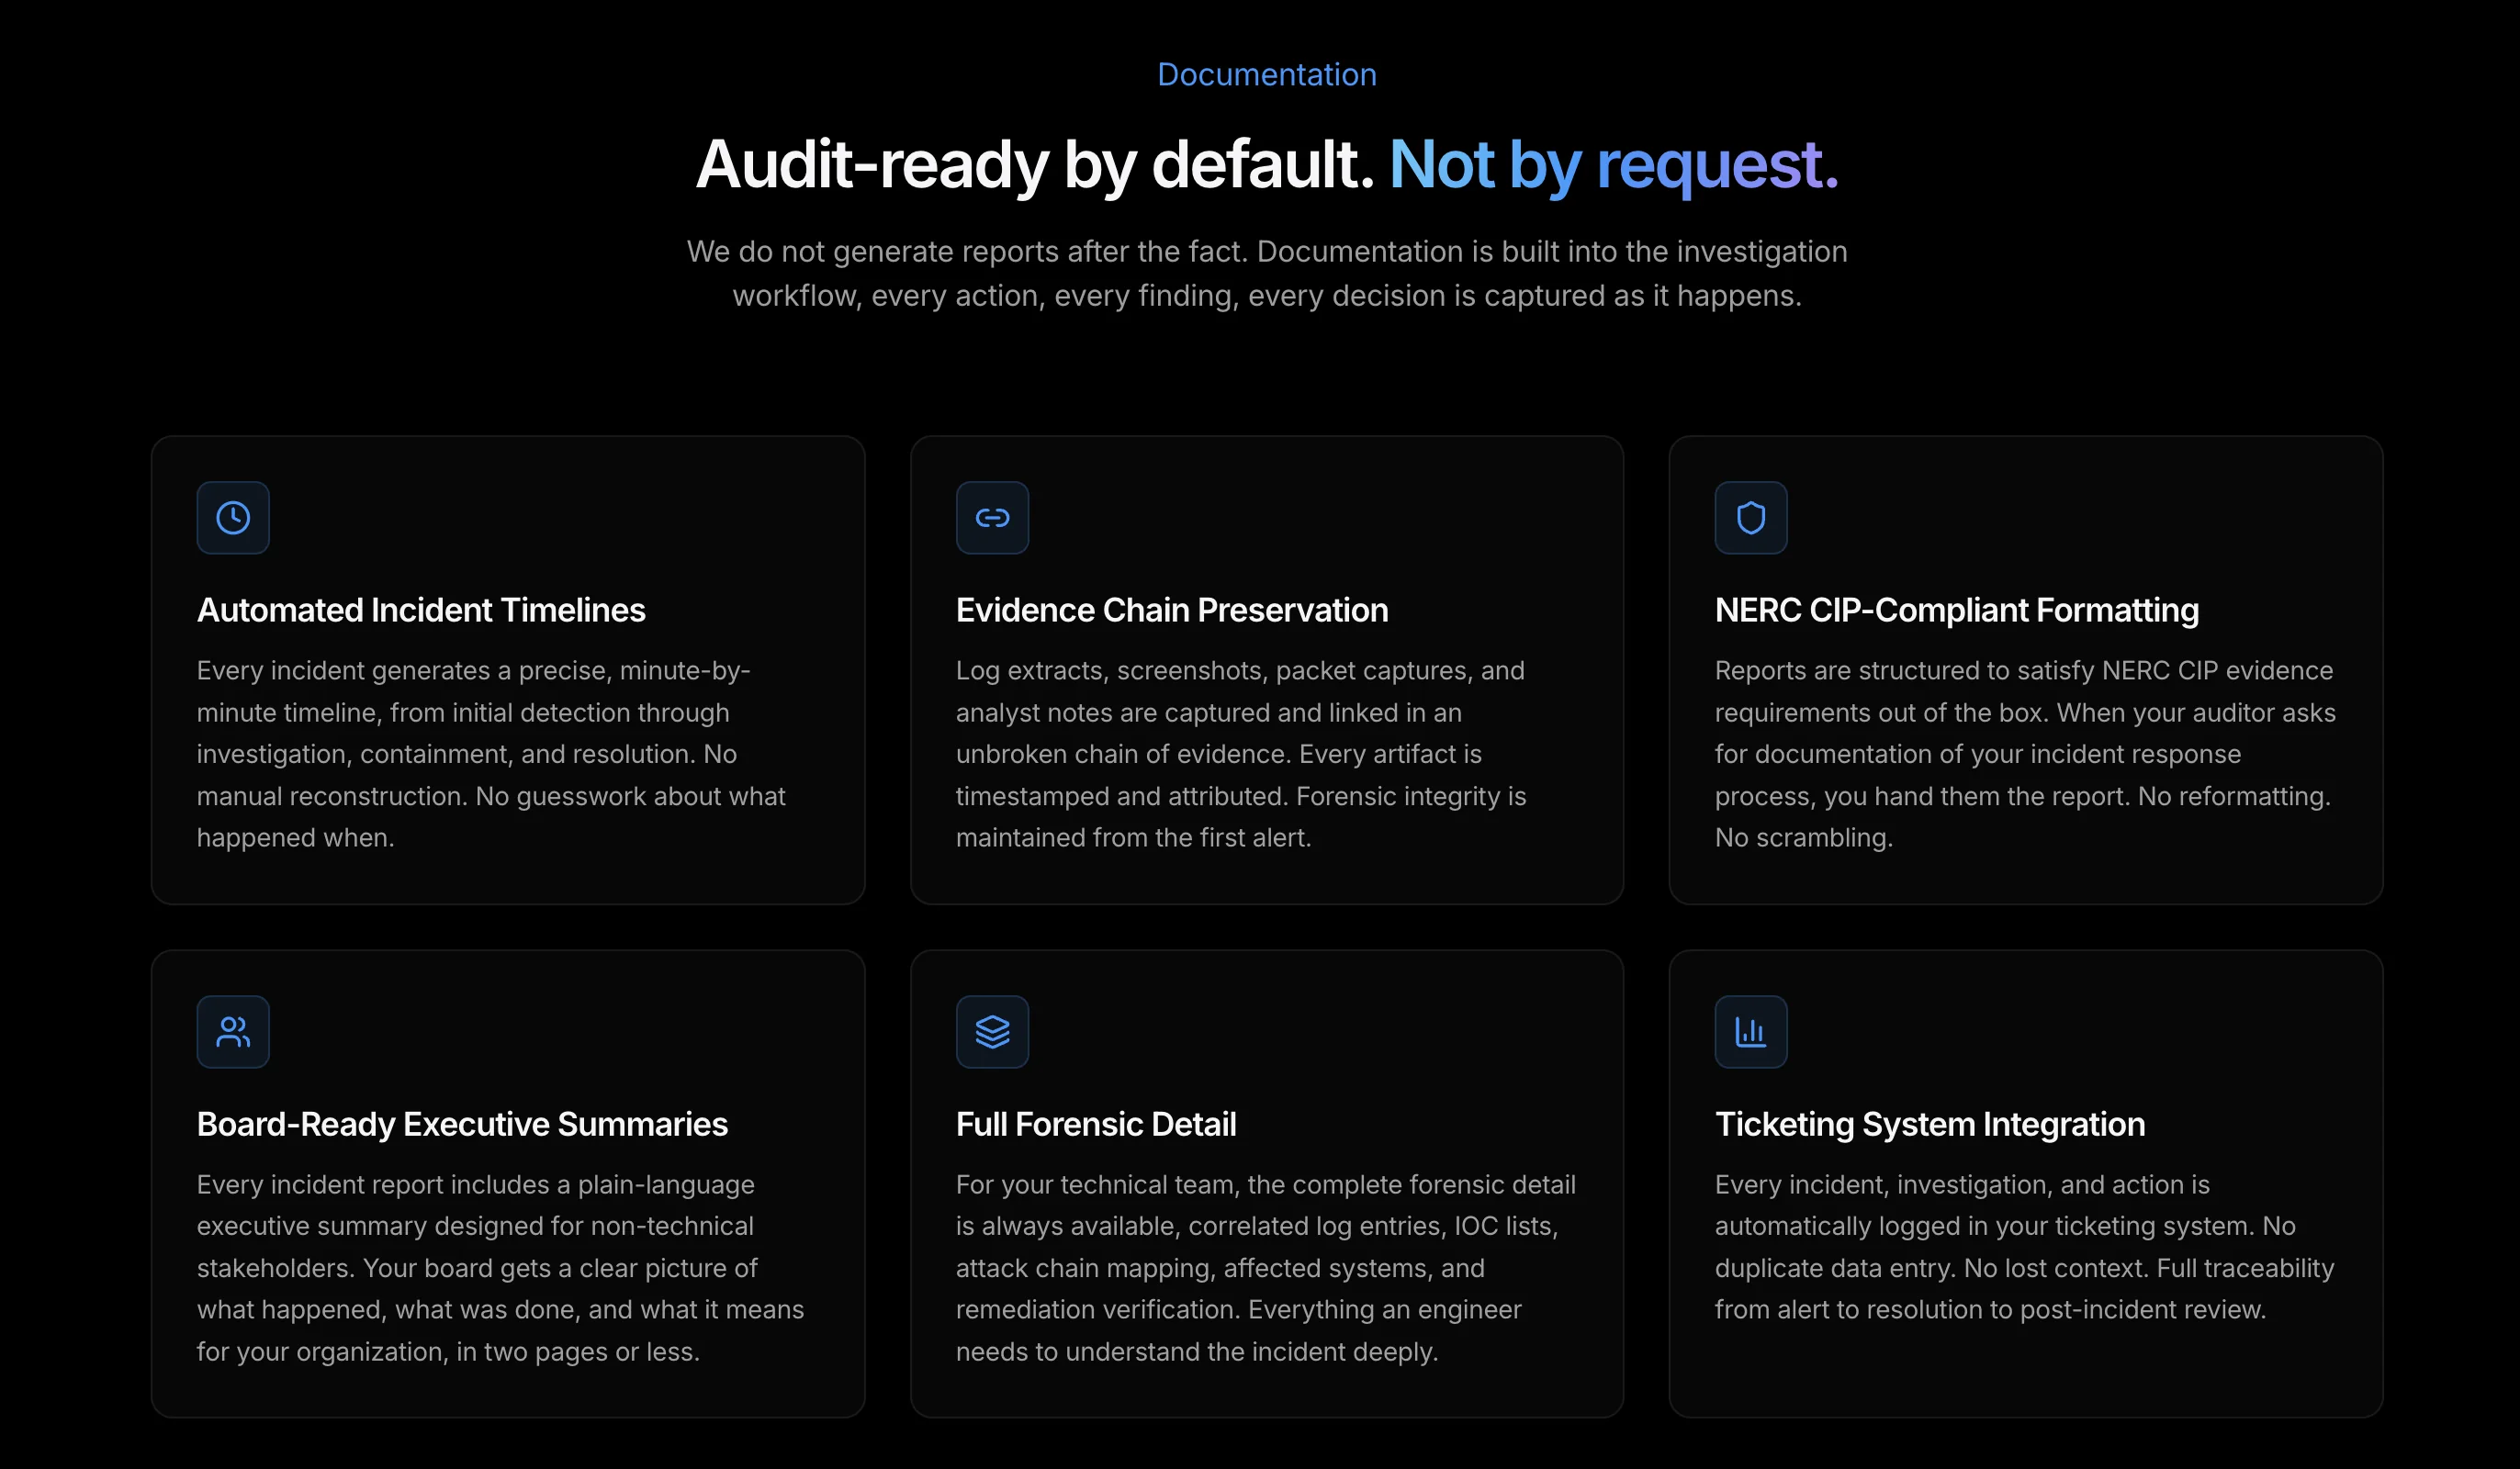
Ready to protect your organization?
Talk to our team about how TITAN and our 24/7 SOC can secure your infrastructure, without the enterprise price tag or complexity.